Deploy from your AI assistant
Your AI assistant. Your people's rules.
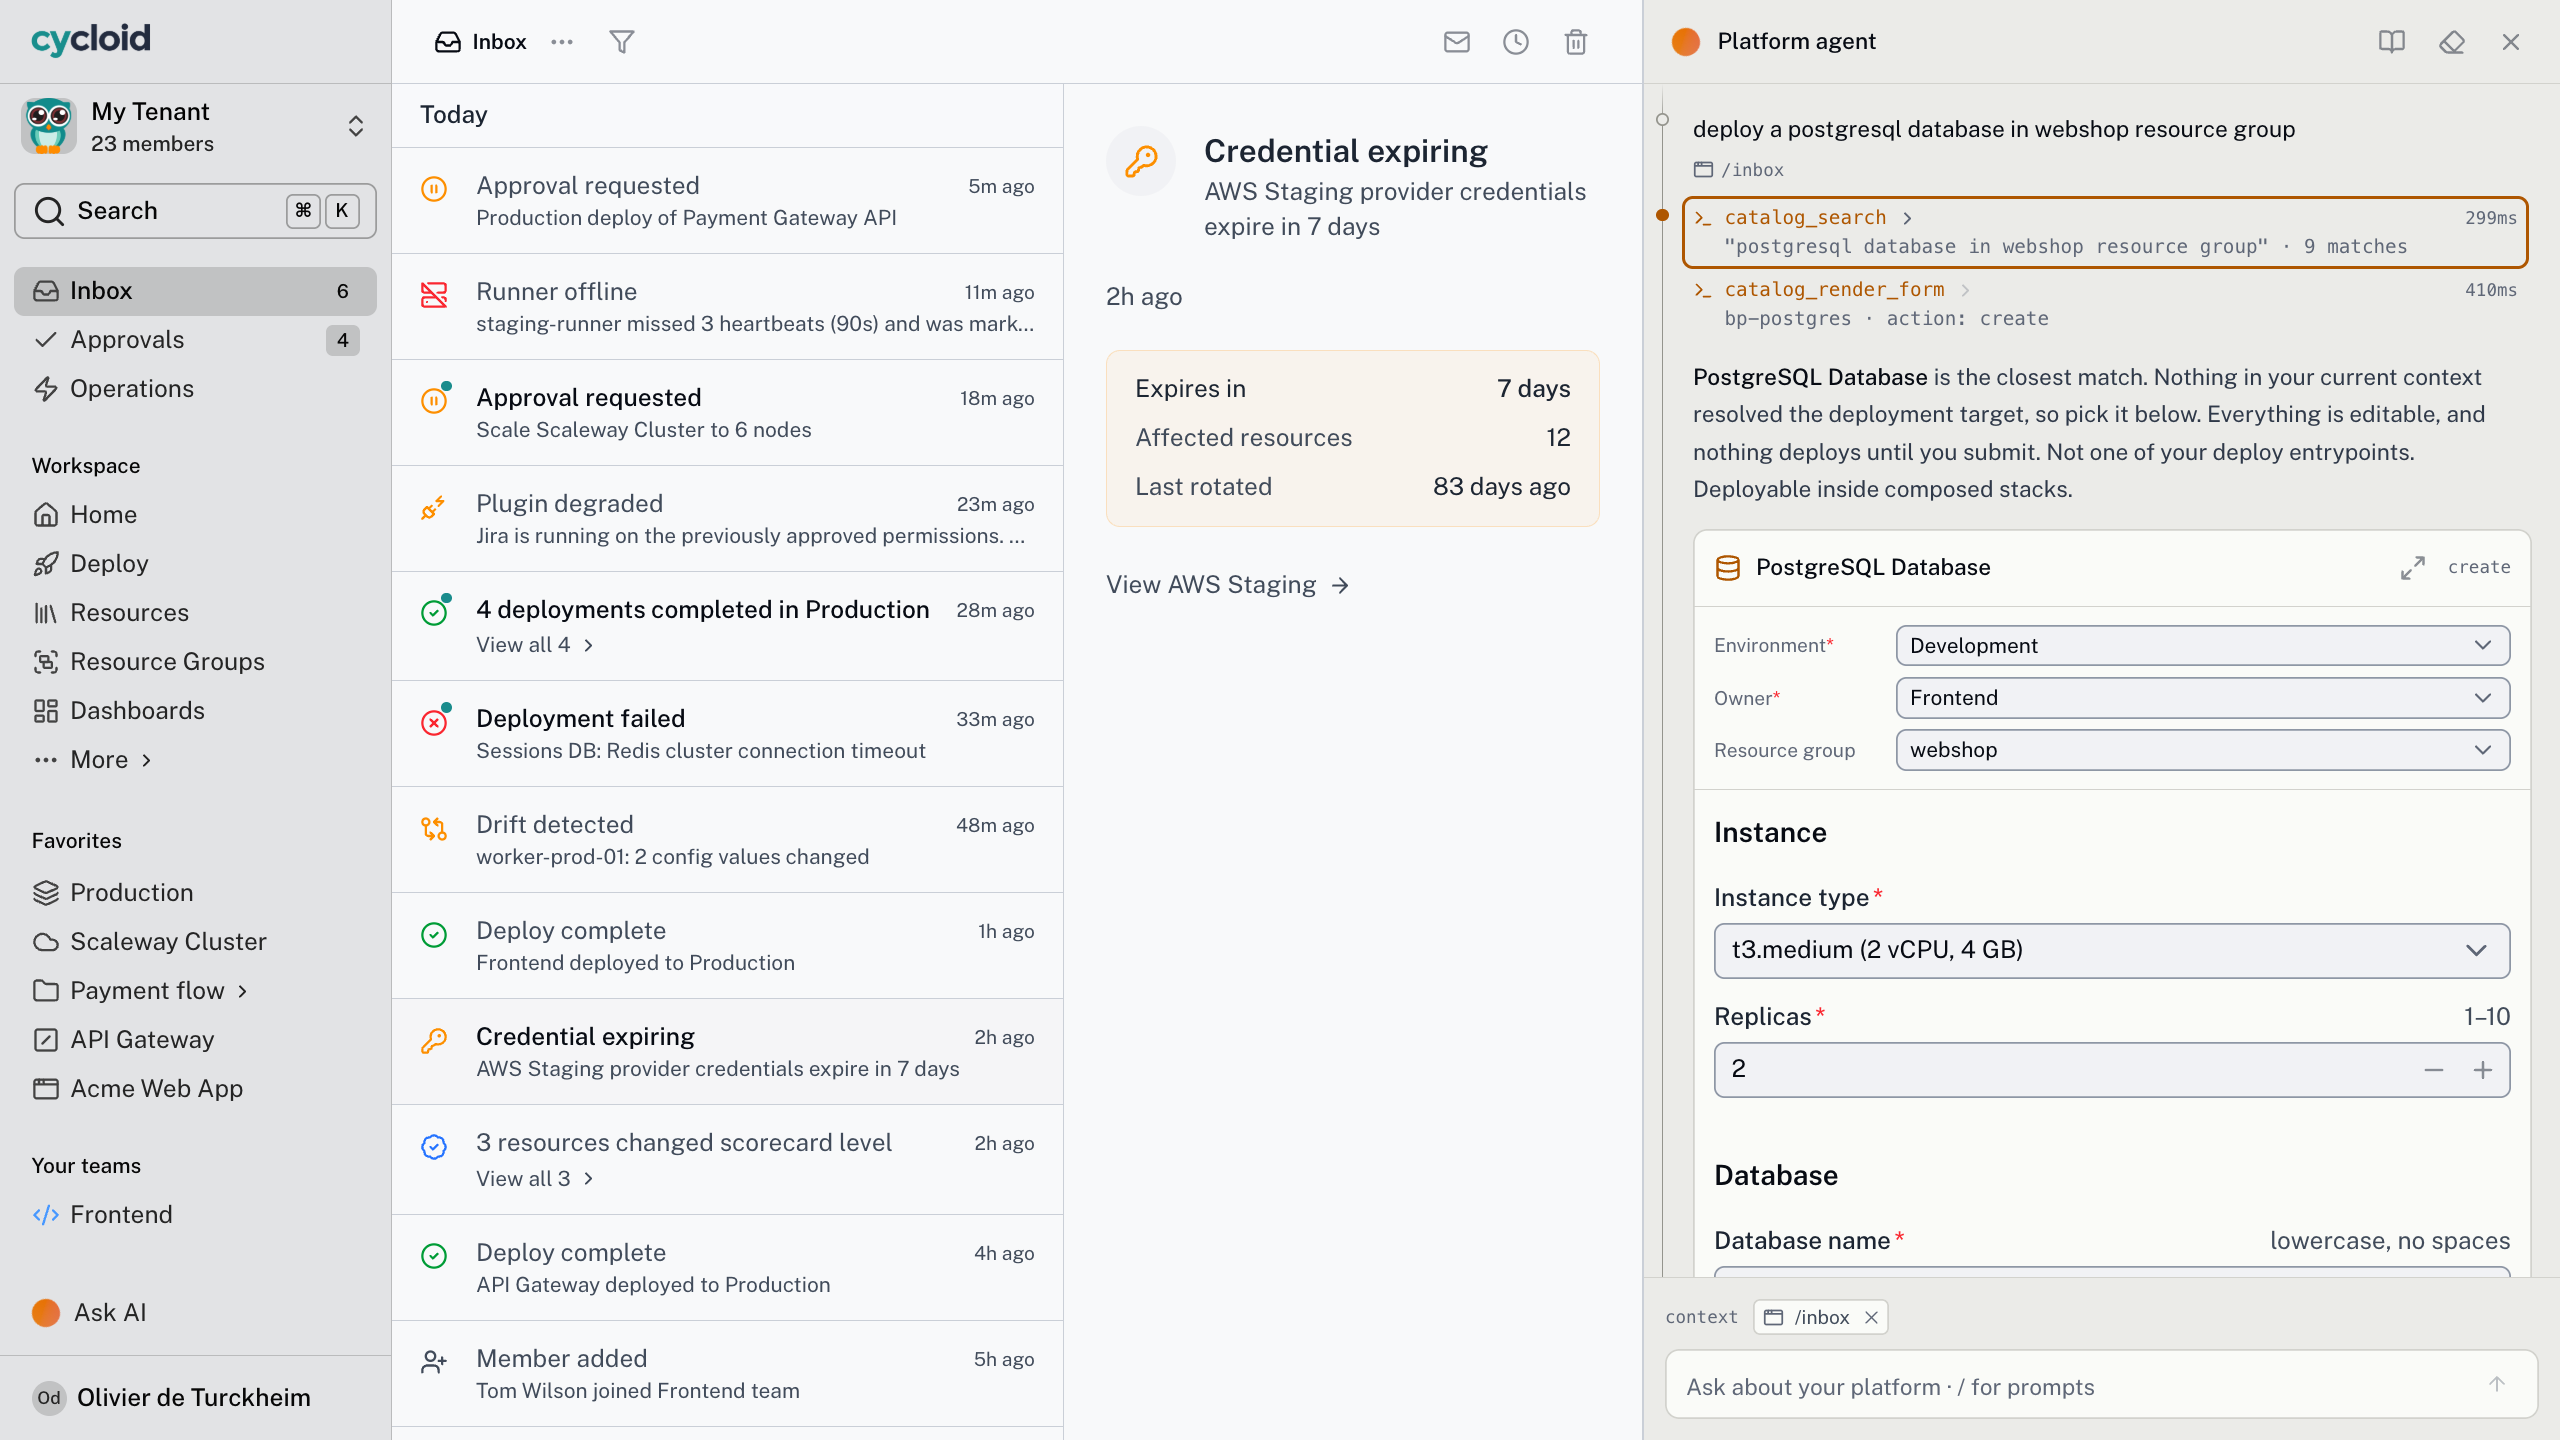
Cycloid’s own assistant and any MCP host you already use run Forms and Actions through the same policy, authorisation and audit as the portal. Same rules, whoever’s asking.
A Cycloid Form in the assistant conversation
Why this matters now
An assistant is faster, and it won't hesitate
The question is no longer whether assistants touch your infrastructure. It’s whether they touch it through a path you govern. An assistant is tireless, quick and has no career to protect, which is exactly why it needs the same guardrails a person has, not fewer.
Assistants are already reaching in
Teams are wiring AI assistants to live tooling today. Without a governed path they build an ungoverned one: a shell, a raw API token, a script nobody reviews.
It has no career to protect
A person hesitates before deleting production. An assistant won’t, unless the platform makes it ask. Speed without the same checks is how a good intention becomes an incident.
A second path is a liability
An assistant deploying outside your policy and audit is shadow IT with an API key. The fix isn’t to ban assistants. It’s to give them the front door.
Cycloid for your team
What deploying from an assistant means for each reader
Give assistants the front door,
not a side one
The problem
Developers will connect assistants to infrastructure with or without you. Every ungoverned connection is a gap you own.
With Cycloid
Assistants deploy through the same Blueprints, Forms and policy as everyone else. One governed path, whether it’s Cycloid’s own assistant or your own host.
The outcome
AI in the platform without a new class of shadow IT to chase down later.
Deploy and fix without leaving the conversation
The problem
Switching from your assistant to a portal to deploy breaks the flow you came for.
With Cycloid
Ask Cycloid’s own assistant, or your editor’s assistant, for an environment or a day-2 action. It runs the governed Form and the Action, inside the rules.
The outcome
Self-service from the chat, with the guardrails still on.
AI in the platform, without a new attack surface
The problem
Agentic automation is arriving whether or not it’s governed, and an ungoverned one is an audit finding waiting to happen.
With Cycloid
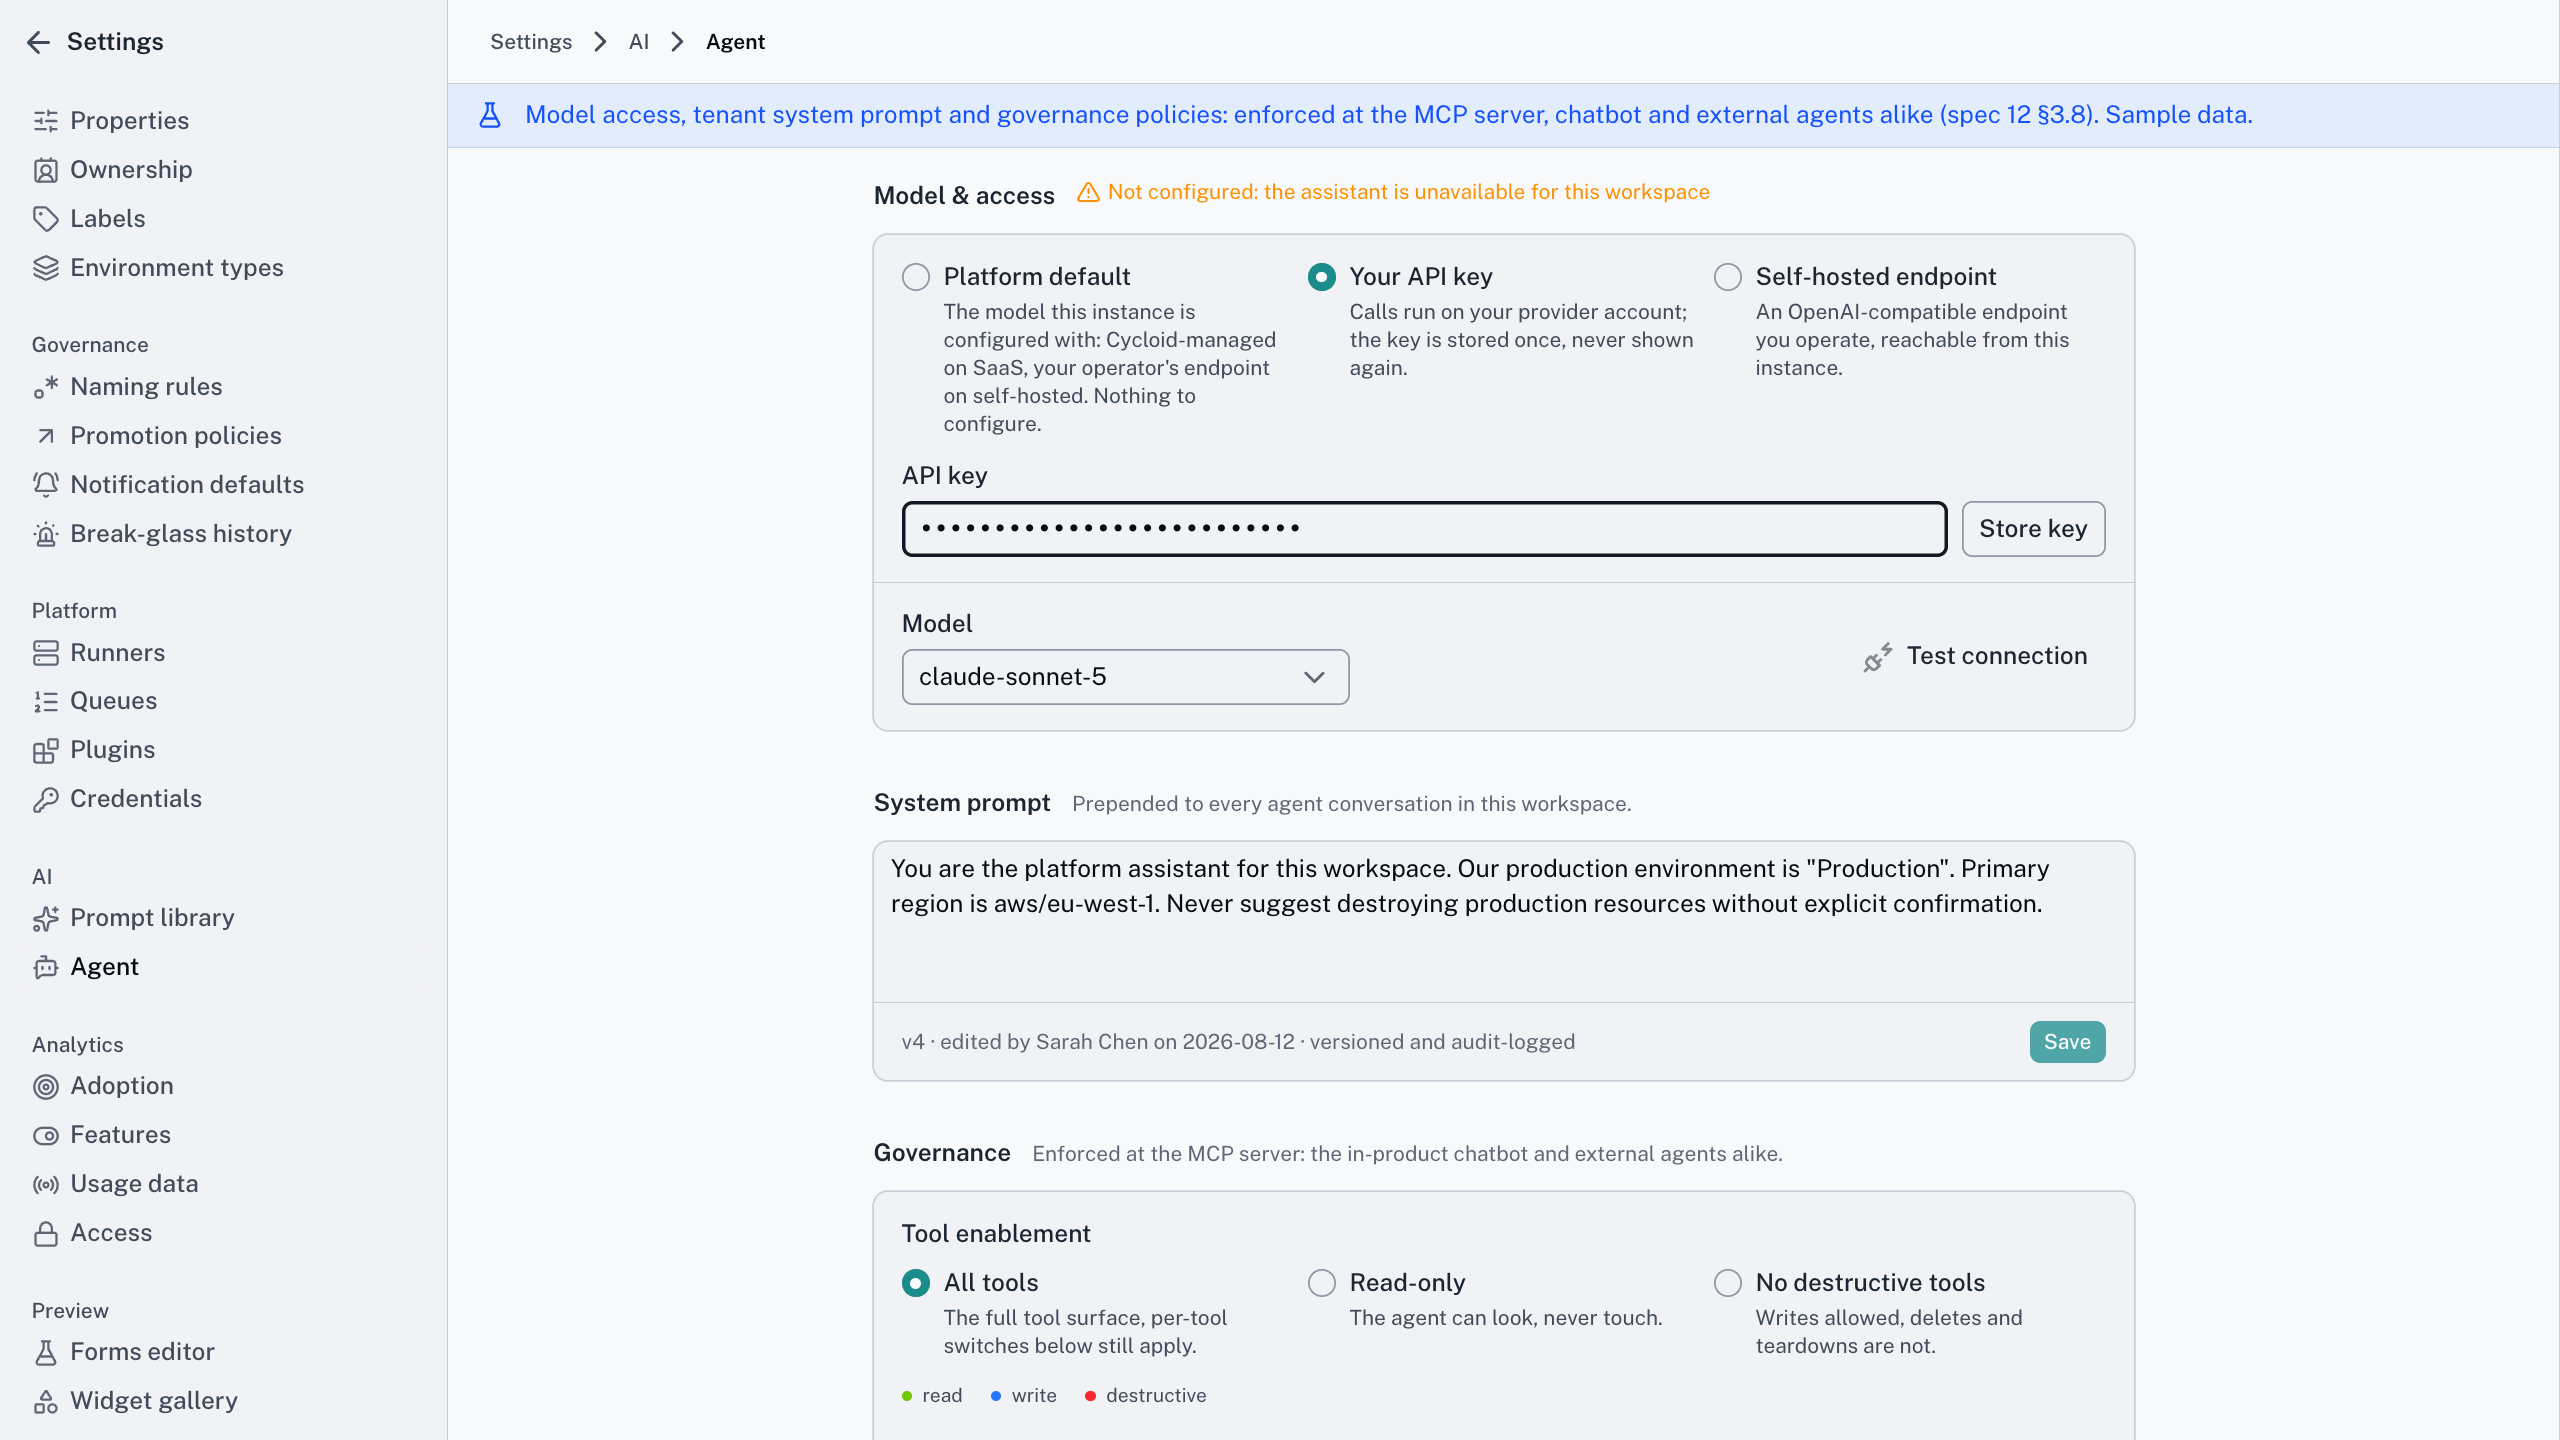
One identity model covers people and assistants. Assistants can be held to tighter limits, and every action is audited as AI.
The outcome
You adopt AI in delivery with a control story you can take to the board.
How it works
The same front door, opened by an assistant
01 · The MCP server exposes the platform
Browse the catalog, render a Form, create a resource, run a day-2 action. Each is a defined tool, never an open shell.
02 · It fills the real Form
Requests go through the platform’s tools, not free text the assistant invents. Cycloid’s assistant shows the Form inline, and other hosts follow as they adopt the extension.
03 · It asks before it guesses
When a request matches more than one Blueprint, the assistant puts the choice to you before anything is created.
04 · The same chain runs, and it can be tighter
Every Action passes ReBAC, RBAC, ABAC and approval. At the tool layer you can hold an assistant below its operator’s rights, read-only or no destroy.
05 · It's recorded as AI
Every action records an actor type and who the assistant acted for, so AI-initiated work is queryable on its own.
Plenty of platforms let an assistant read. The harder, more useful half is letting it act, submitting a governed Form that provisions, scales or upgrades real infrastructure through the same policy and audit as the portal. That’s the half Cycloid is built around. A portal shows. We let the assistant do.
The same front door, opened by an assistant
The short version
What an assistant can't get round
4
authorisation layers on every assistant call
3
audit fields per action: what, for whom, which chat
0
shell access. Only defined tools
1
identity model for people and assistants
Frequently asked questions
Cycloid’s own built-in assistant, plus any MCP-capable host, such as Claude Desktop, Cursor or a custom assistant. Governed tool calls work from all of them, and Forms render inline wherever the host supports it.
No. An assistant runs the same four-layer chain as the person behind it, and you can scope it tighter at the tool layer, read-only with no destroy, say. There’s no automation path around the rules.
Every action records an actor type and an on-behalf-of field. The trail shows that an assistant acted and for which person, so AI-initiated work never blurs into the human log. That’s exactly what your auditors will ask for.
Browse and search the catalog, render a Form, create and update resources, run day-2 actions, and read inventory and approvals. It’s a stable, versioned set of tools, not an open shell.
Watch an assistant deploy, inside your rules
Bring the assistant workflow you’re worried about. In twenty minutes we’ll show the same request going through Cycloid’s governed path, from the conversation to a real environment, with the audit trail to match.