Solutions / Governance & Platform
The guardrails your platform needs, without starting from scratch
Your platform team builds the guardrails once. Developers and AI assistants work inside them without asking, and every request gets checked before the resource exists. It all runs where you decide.
Platform & DevOps
Developers
The guardrails are inside the golden path, so you don’t read the policy to comply with it.
Executives
Self-hosted, air-gapped or sovereign cloud, European by design. Nothing here is taken on faith.
Why
Access, audit and where it runs, settled before the resource exists
Your platform team shouldn’t hand-build every environment and then police it afterwards. Set the rules once and they hold for every request, from a person or an assistant. Developers stop waiting on you. The organisation gets delivery that’s compliant on arrival, not checked after the fact.
Without it
Audit as archaeology
Policy is a document, enforcement is a review, and the finding arrives a quarter after the resource did. Rights are copied from whoever left last.
Signs it’s your problem
- A compliance finding names a resource nobody approved
- Access rights are inherited from the last person who had the job
- An AI assistant has the same rights as its user, everywhere, unobserved
With Cycloid
Ask first, every time
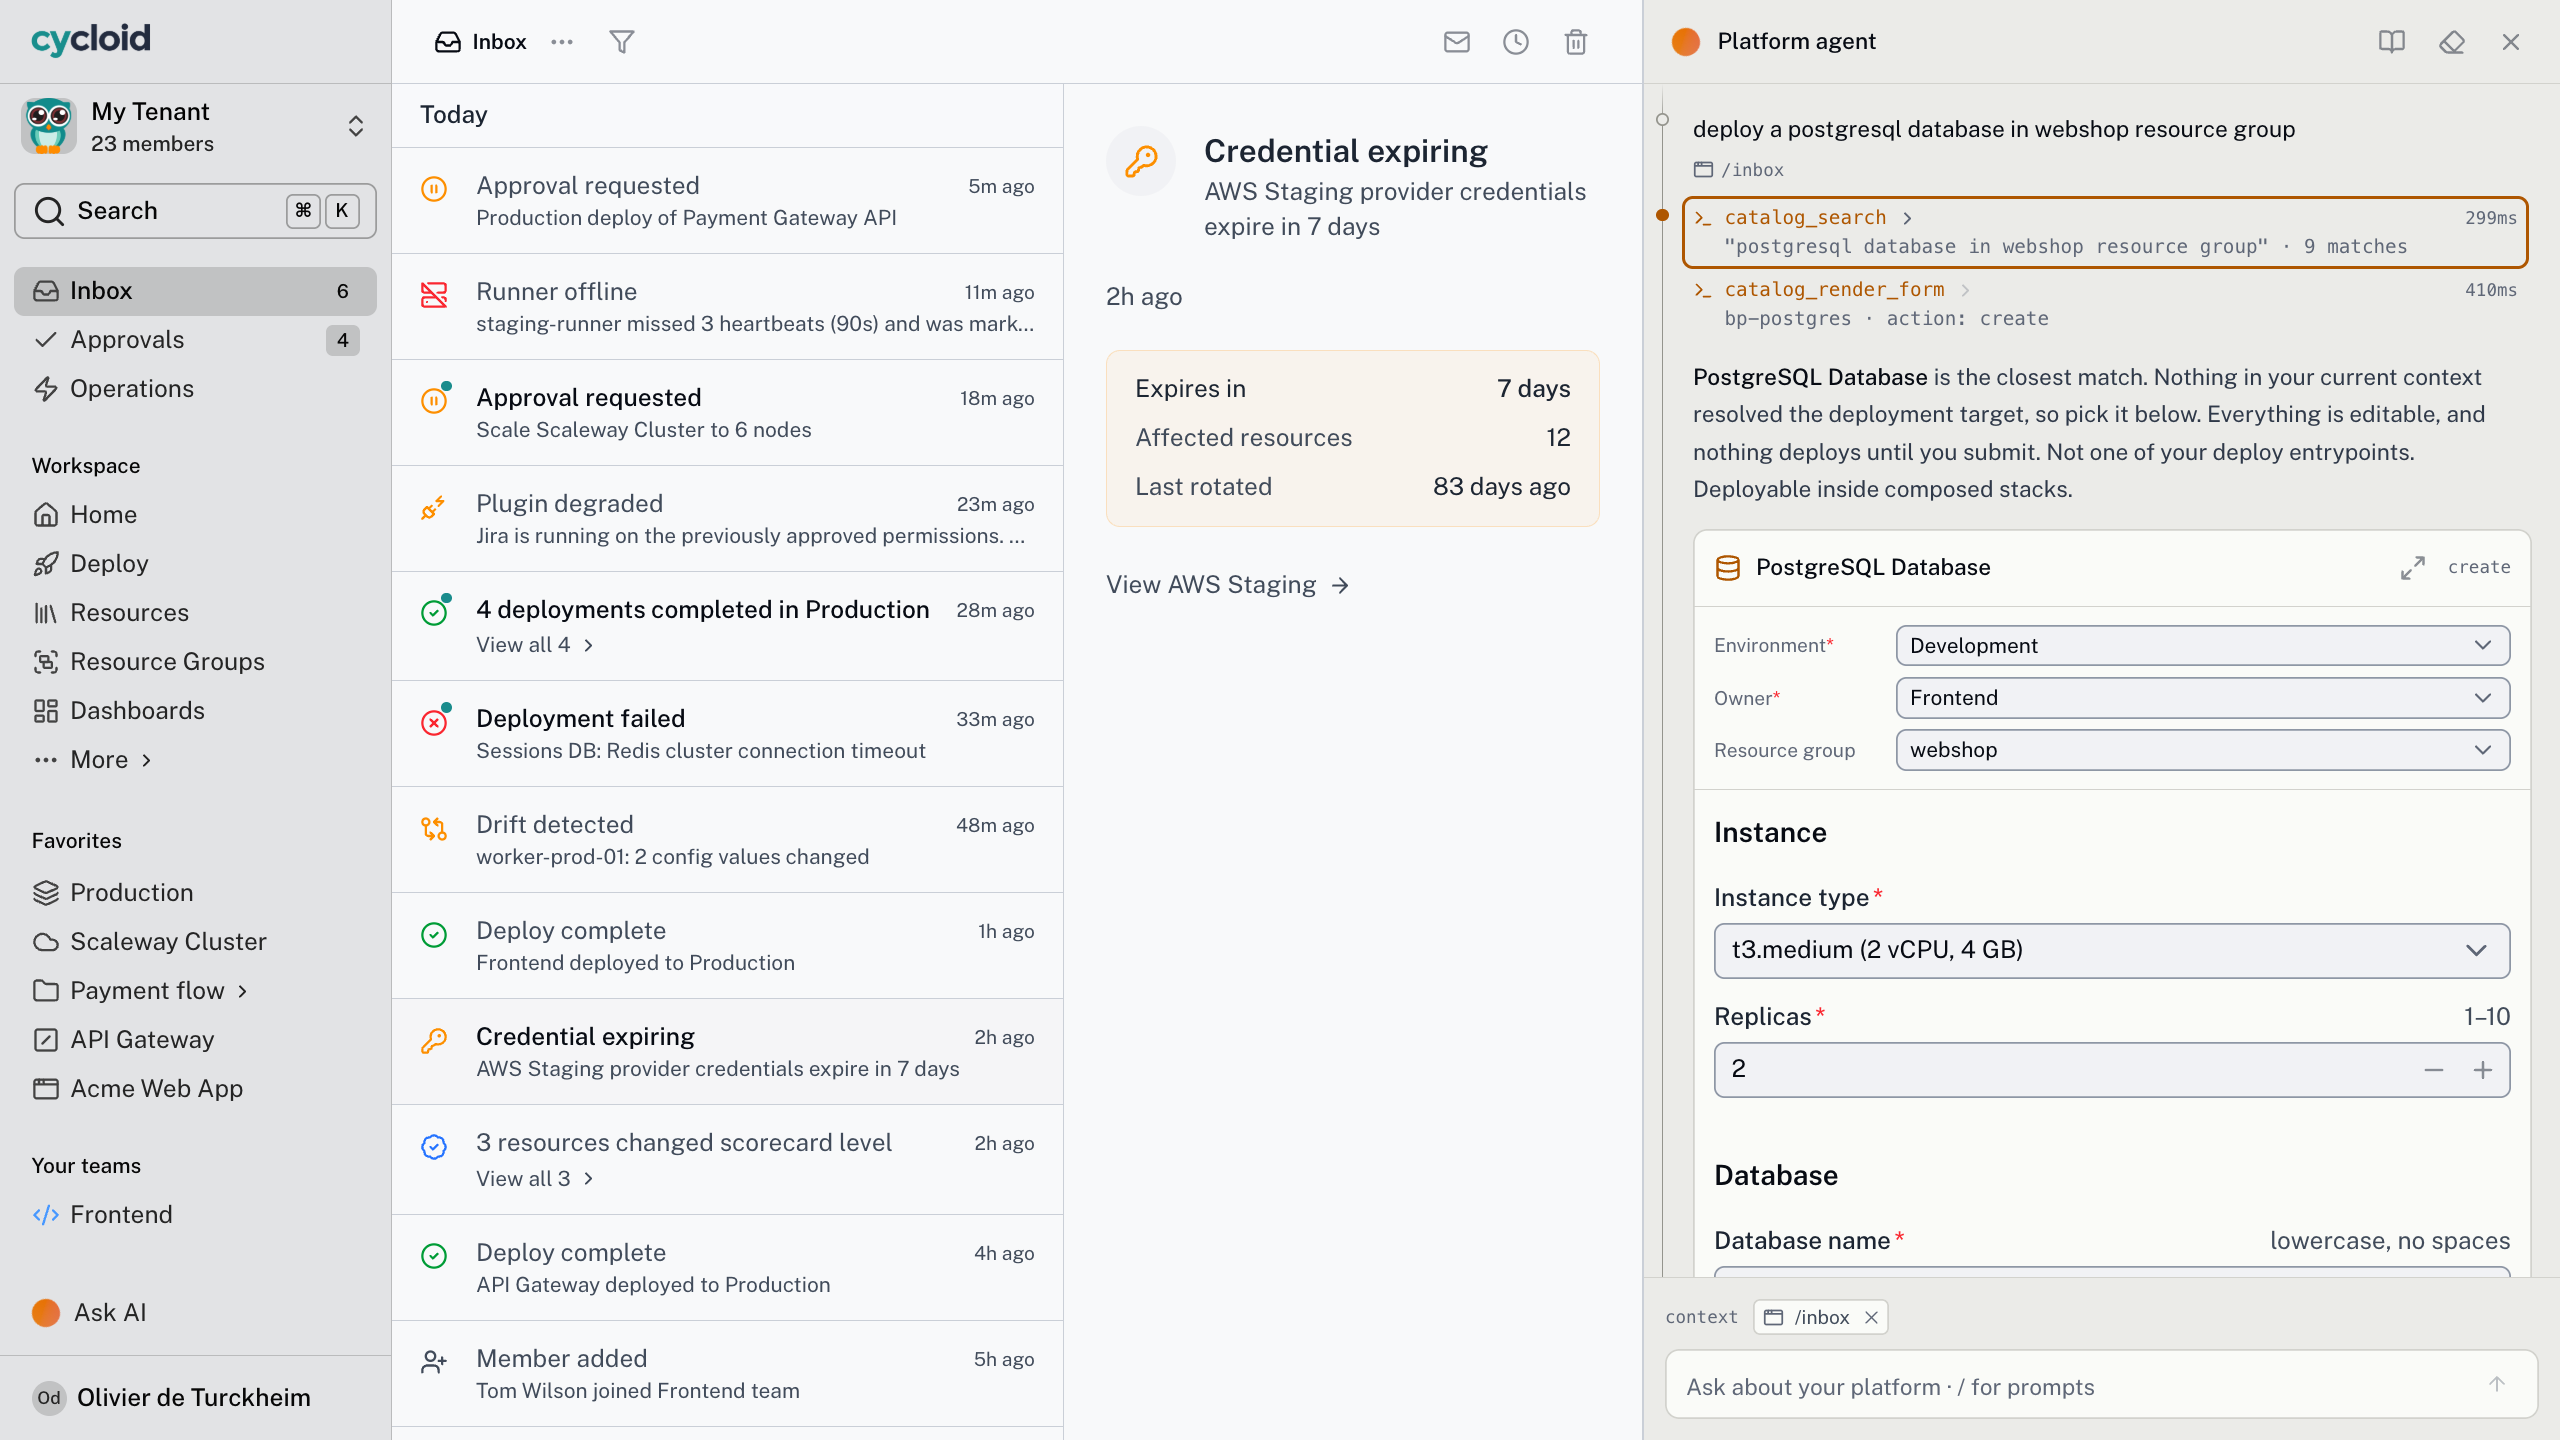
Forms validates every submission. Approval gates run before a deployment. Every Action, from a person or an assistant, passes the same four-layer authorisation chain and lands in the audit trail.
What changes
- A non-compliant resource is refused before it exists
- An assistant can be scoped tighter than its user, read-only or no destroy
- One record answers the auditor, and everyone else
The trade-off · speed vs compliance · guardrails before the resource keep both
How
Four steps to guardrails everyone can work inside
Four steps, each with a page of its own. Where it runs first, then who may do what, then the environments, then the record of it.
What
Eight features that make the guardrails
Each has a page of its own. Here’s what it does, how, and who it’s for.
In this pillar
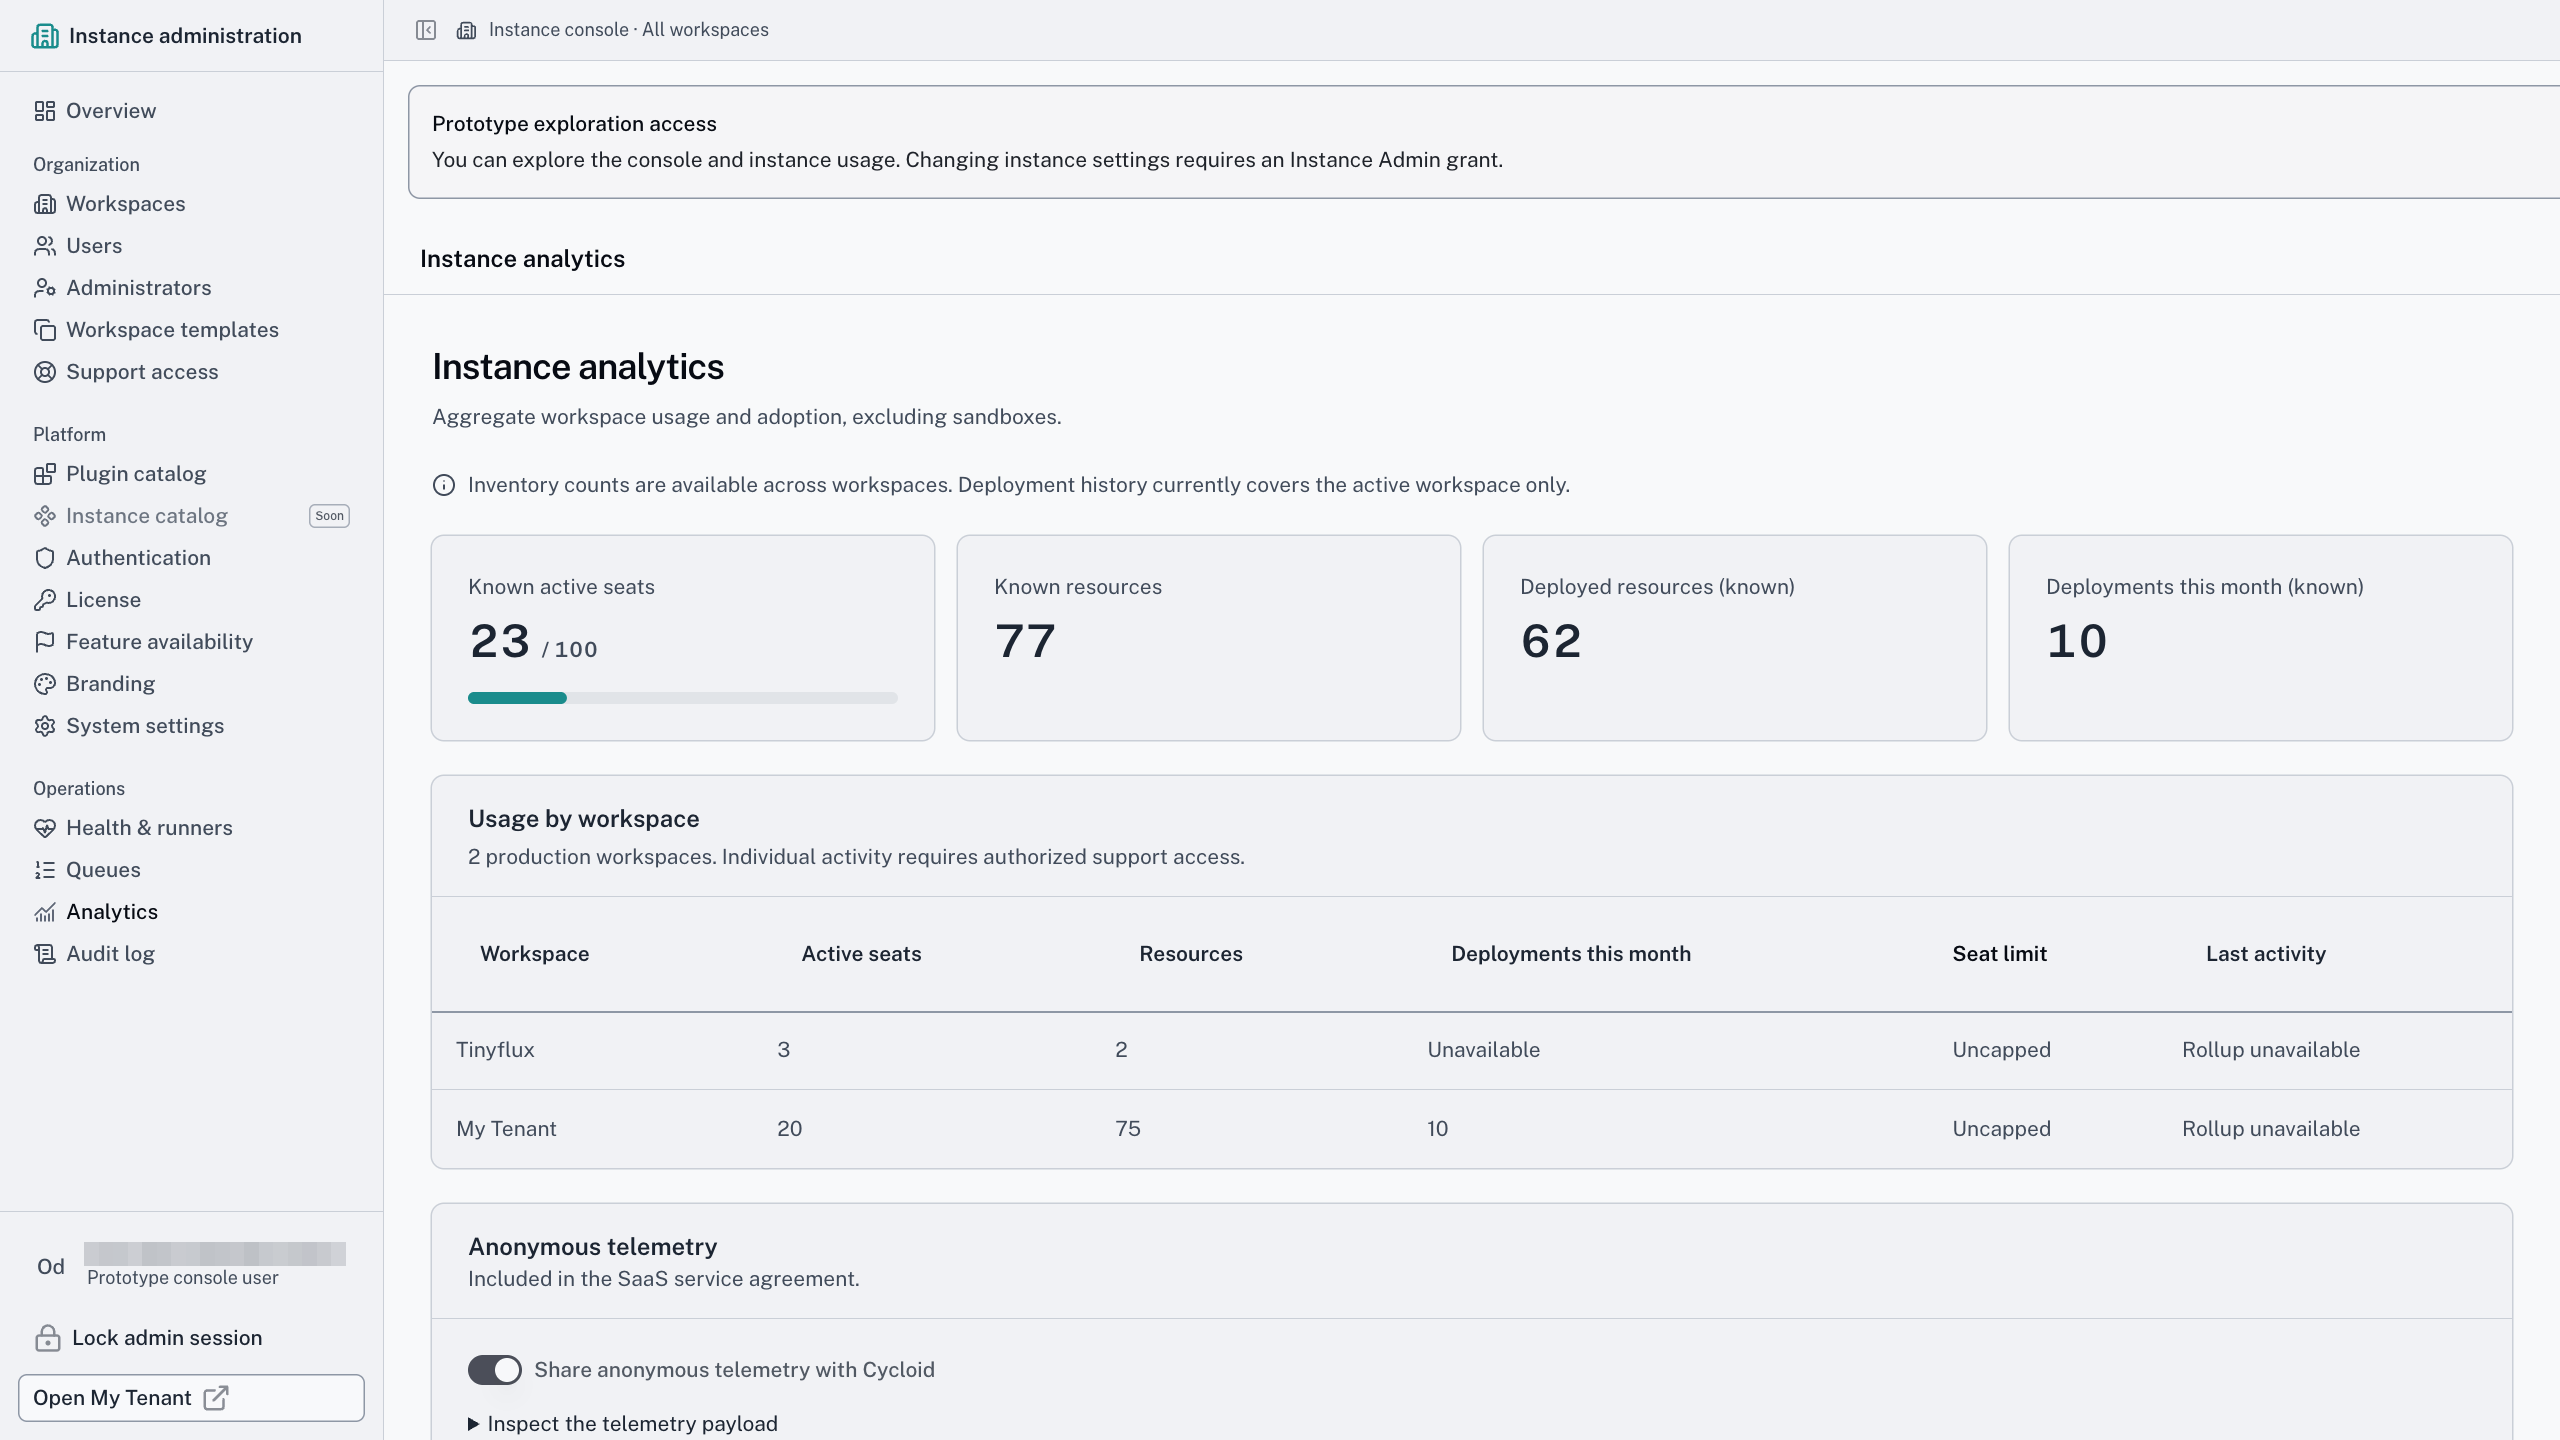
Self-hosted, air-gapped, sovereign
Deploys where your data has to stay, on a hyperscaler, a private cloud or fully disconnected, with licence validation that works offline.
Self-hosted first, European by design, ISO 27001 certified, open formats. TerraCognita and InfraMap are open source.
Built for
Executives
Platform & DevOps
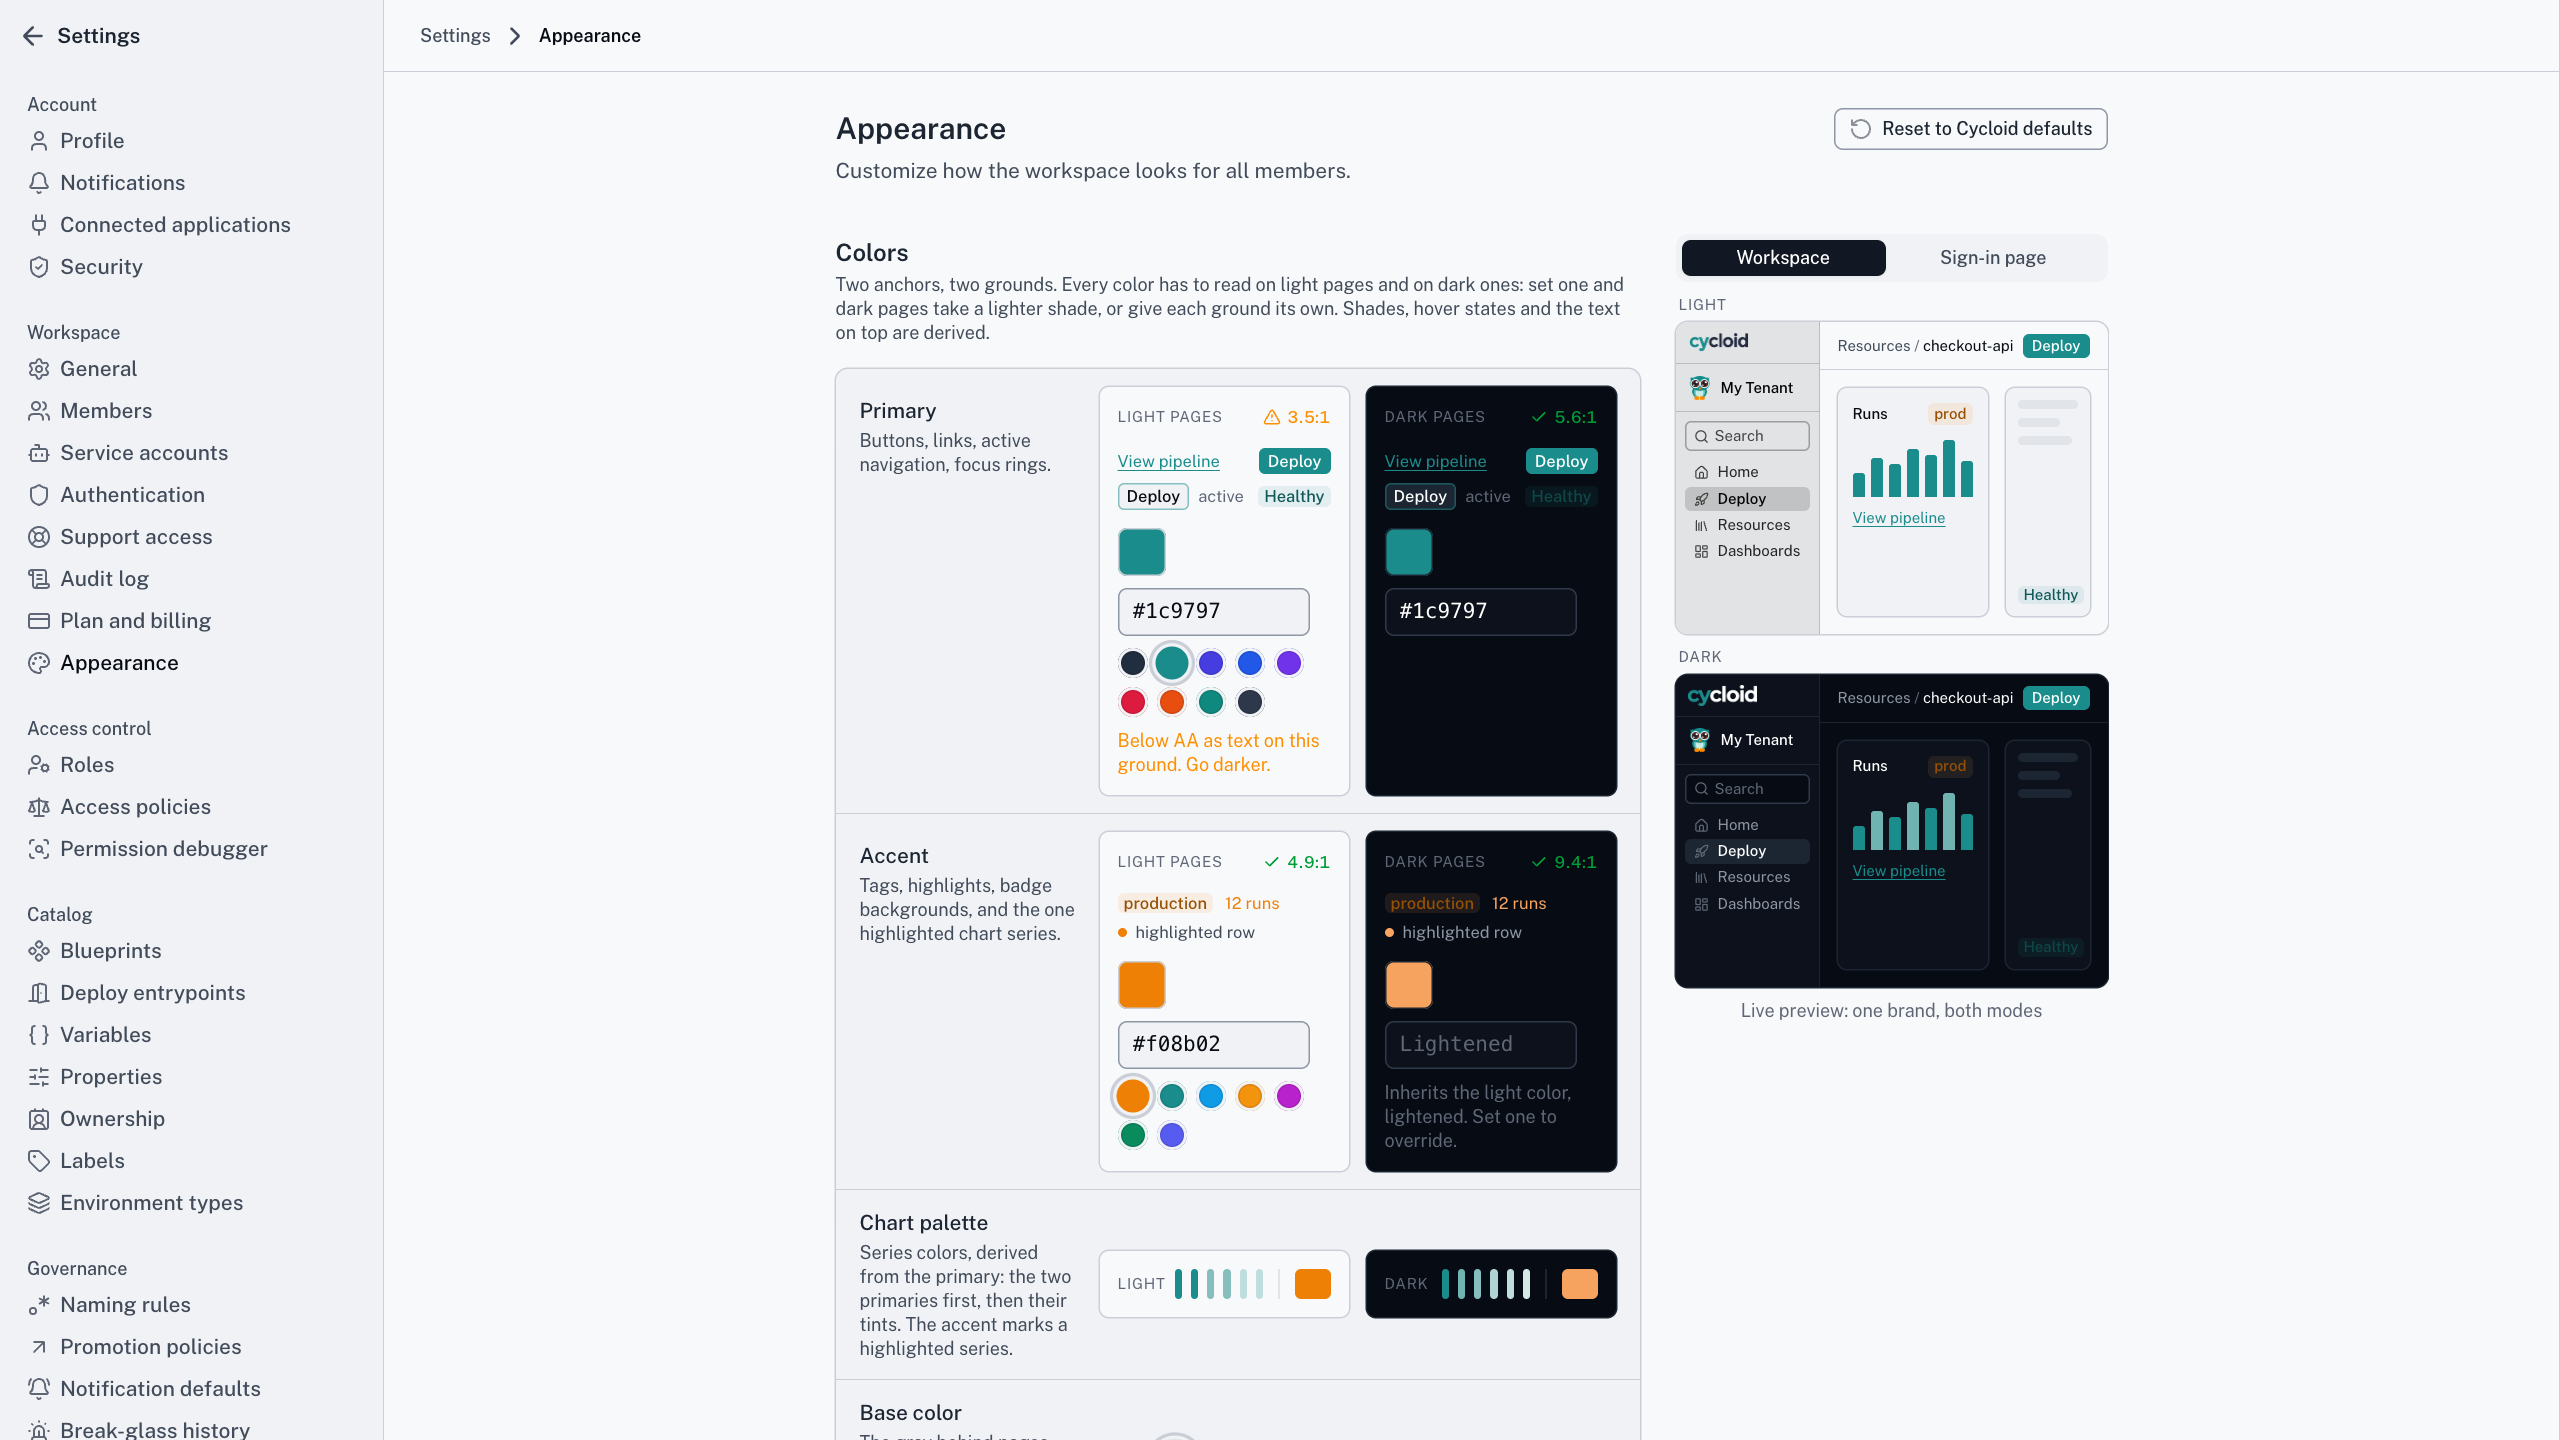
Customisable portal
Built for
Platform & DevOps
Developers
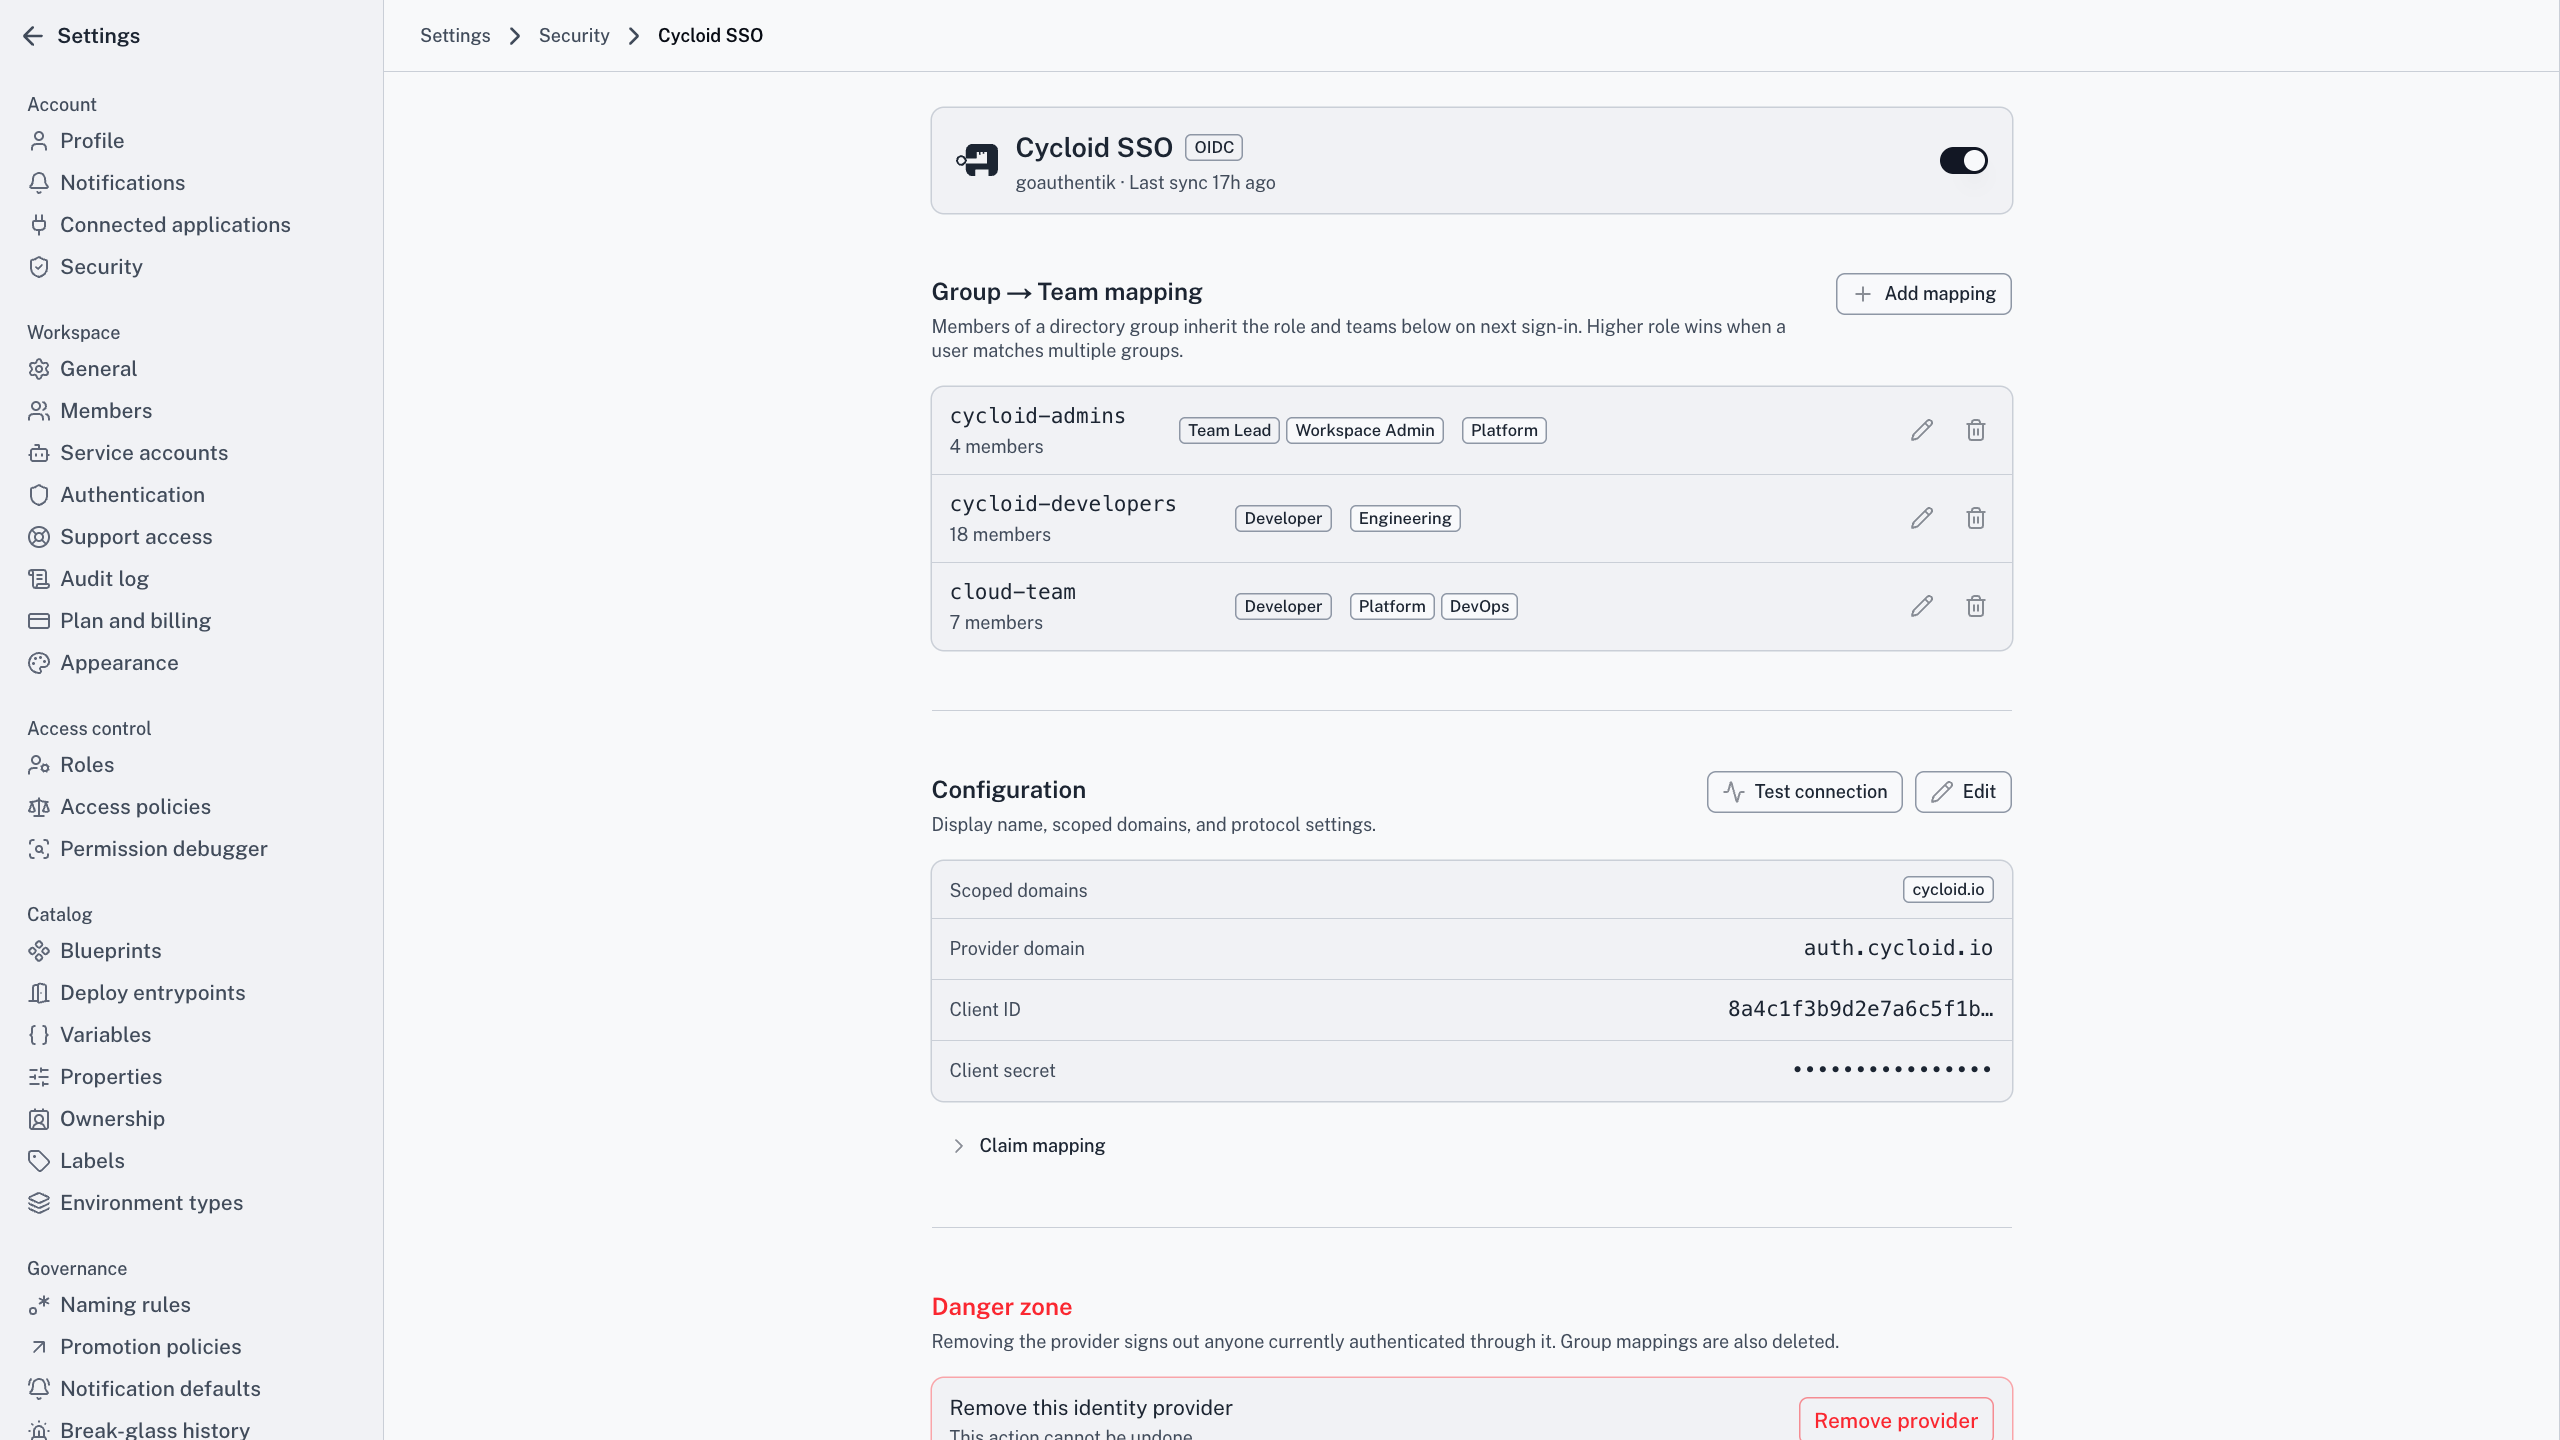
Org modelling & SSO
Maps teams, roles and Resource Groups onto your org, with isolated tenants for MSPs.
SSO through Entra ID, Okta, Keycloak or any OIDC or SAML 2.0 IdP, with SCIM.
Built for
Platform & DevOps
Executives
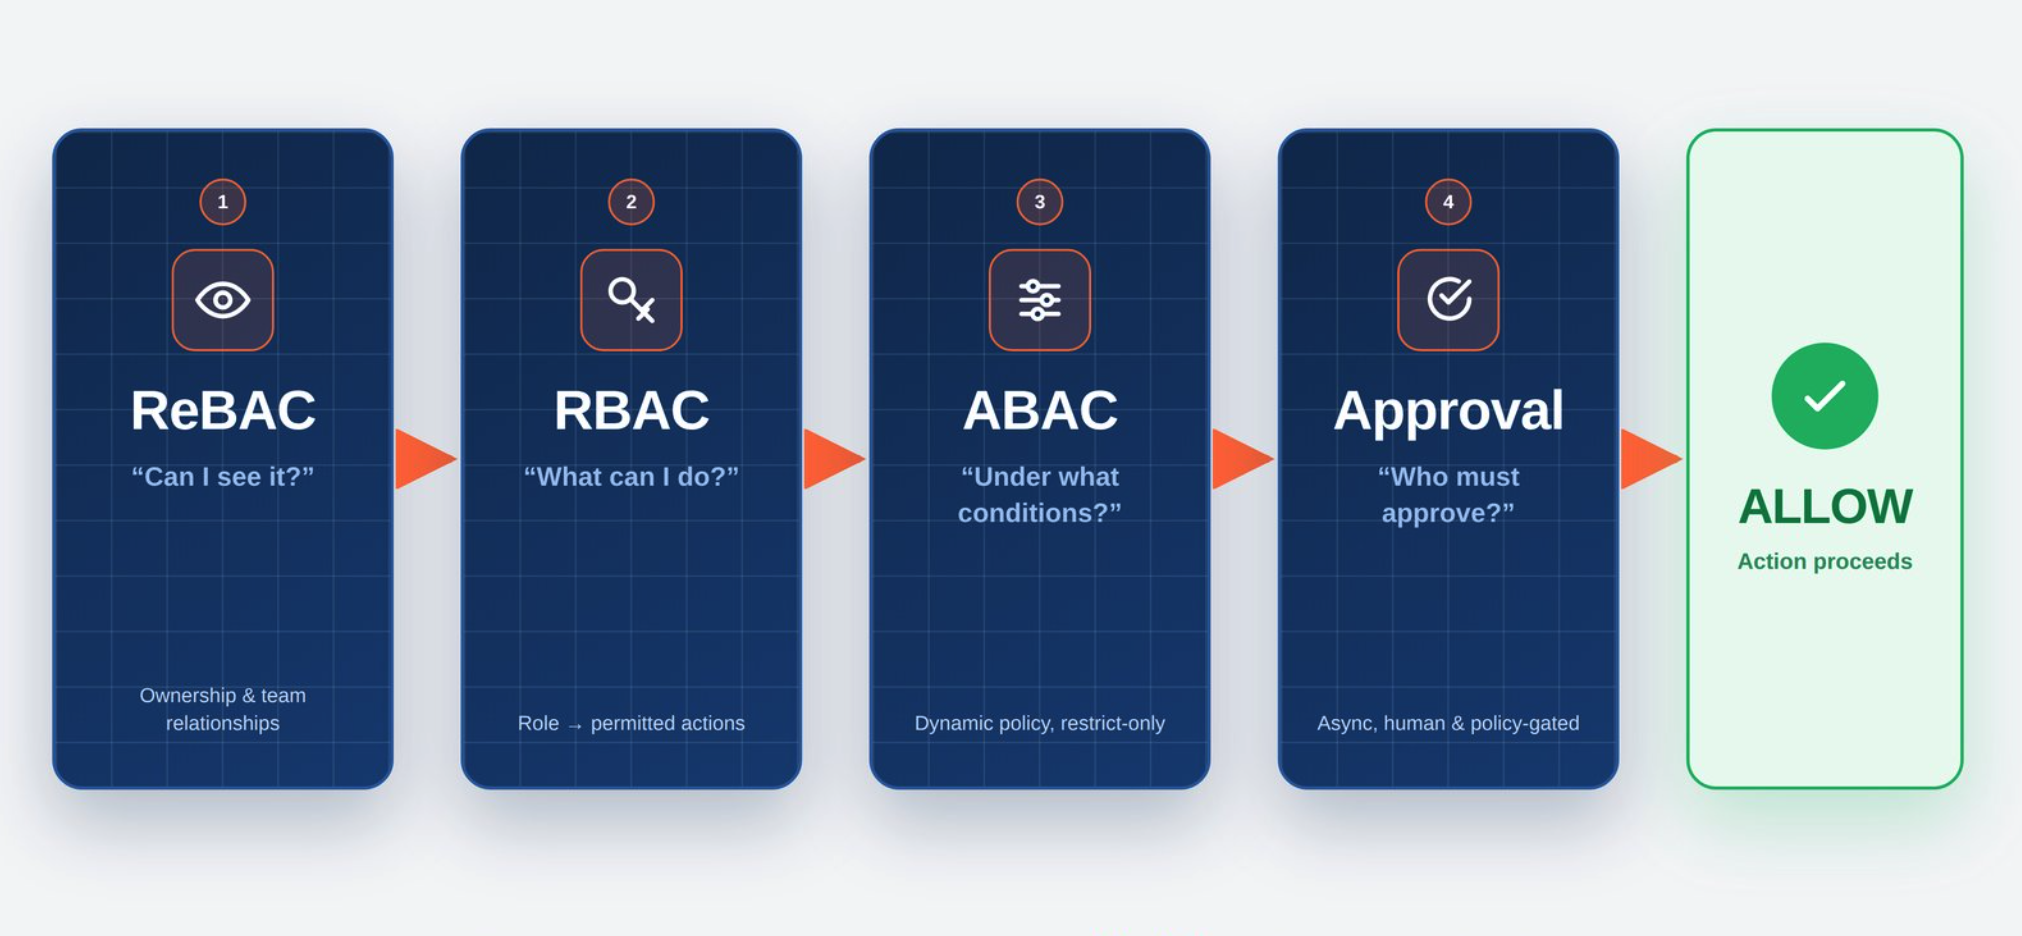
Four-layer authorisation
Runs every decision through four layers, ReBAC, RBAC, ABAC and approval. All four must say yes.
Built on OpenFGA. An assistant can be held tighter than its user at the tool layer.
Built for
Platform & DevOps
Executives
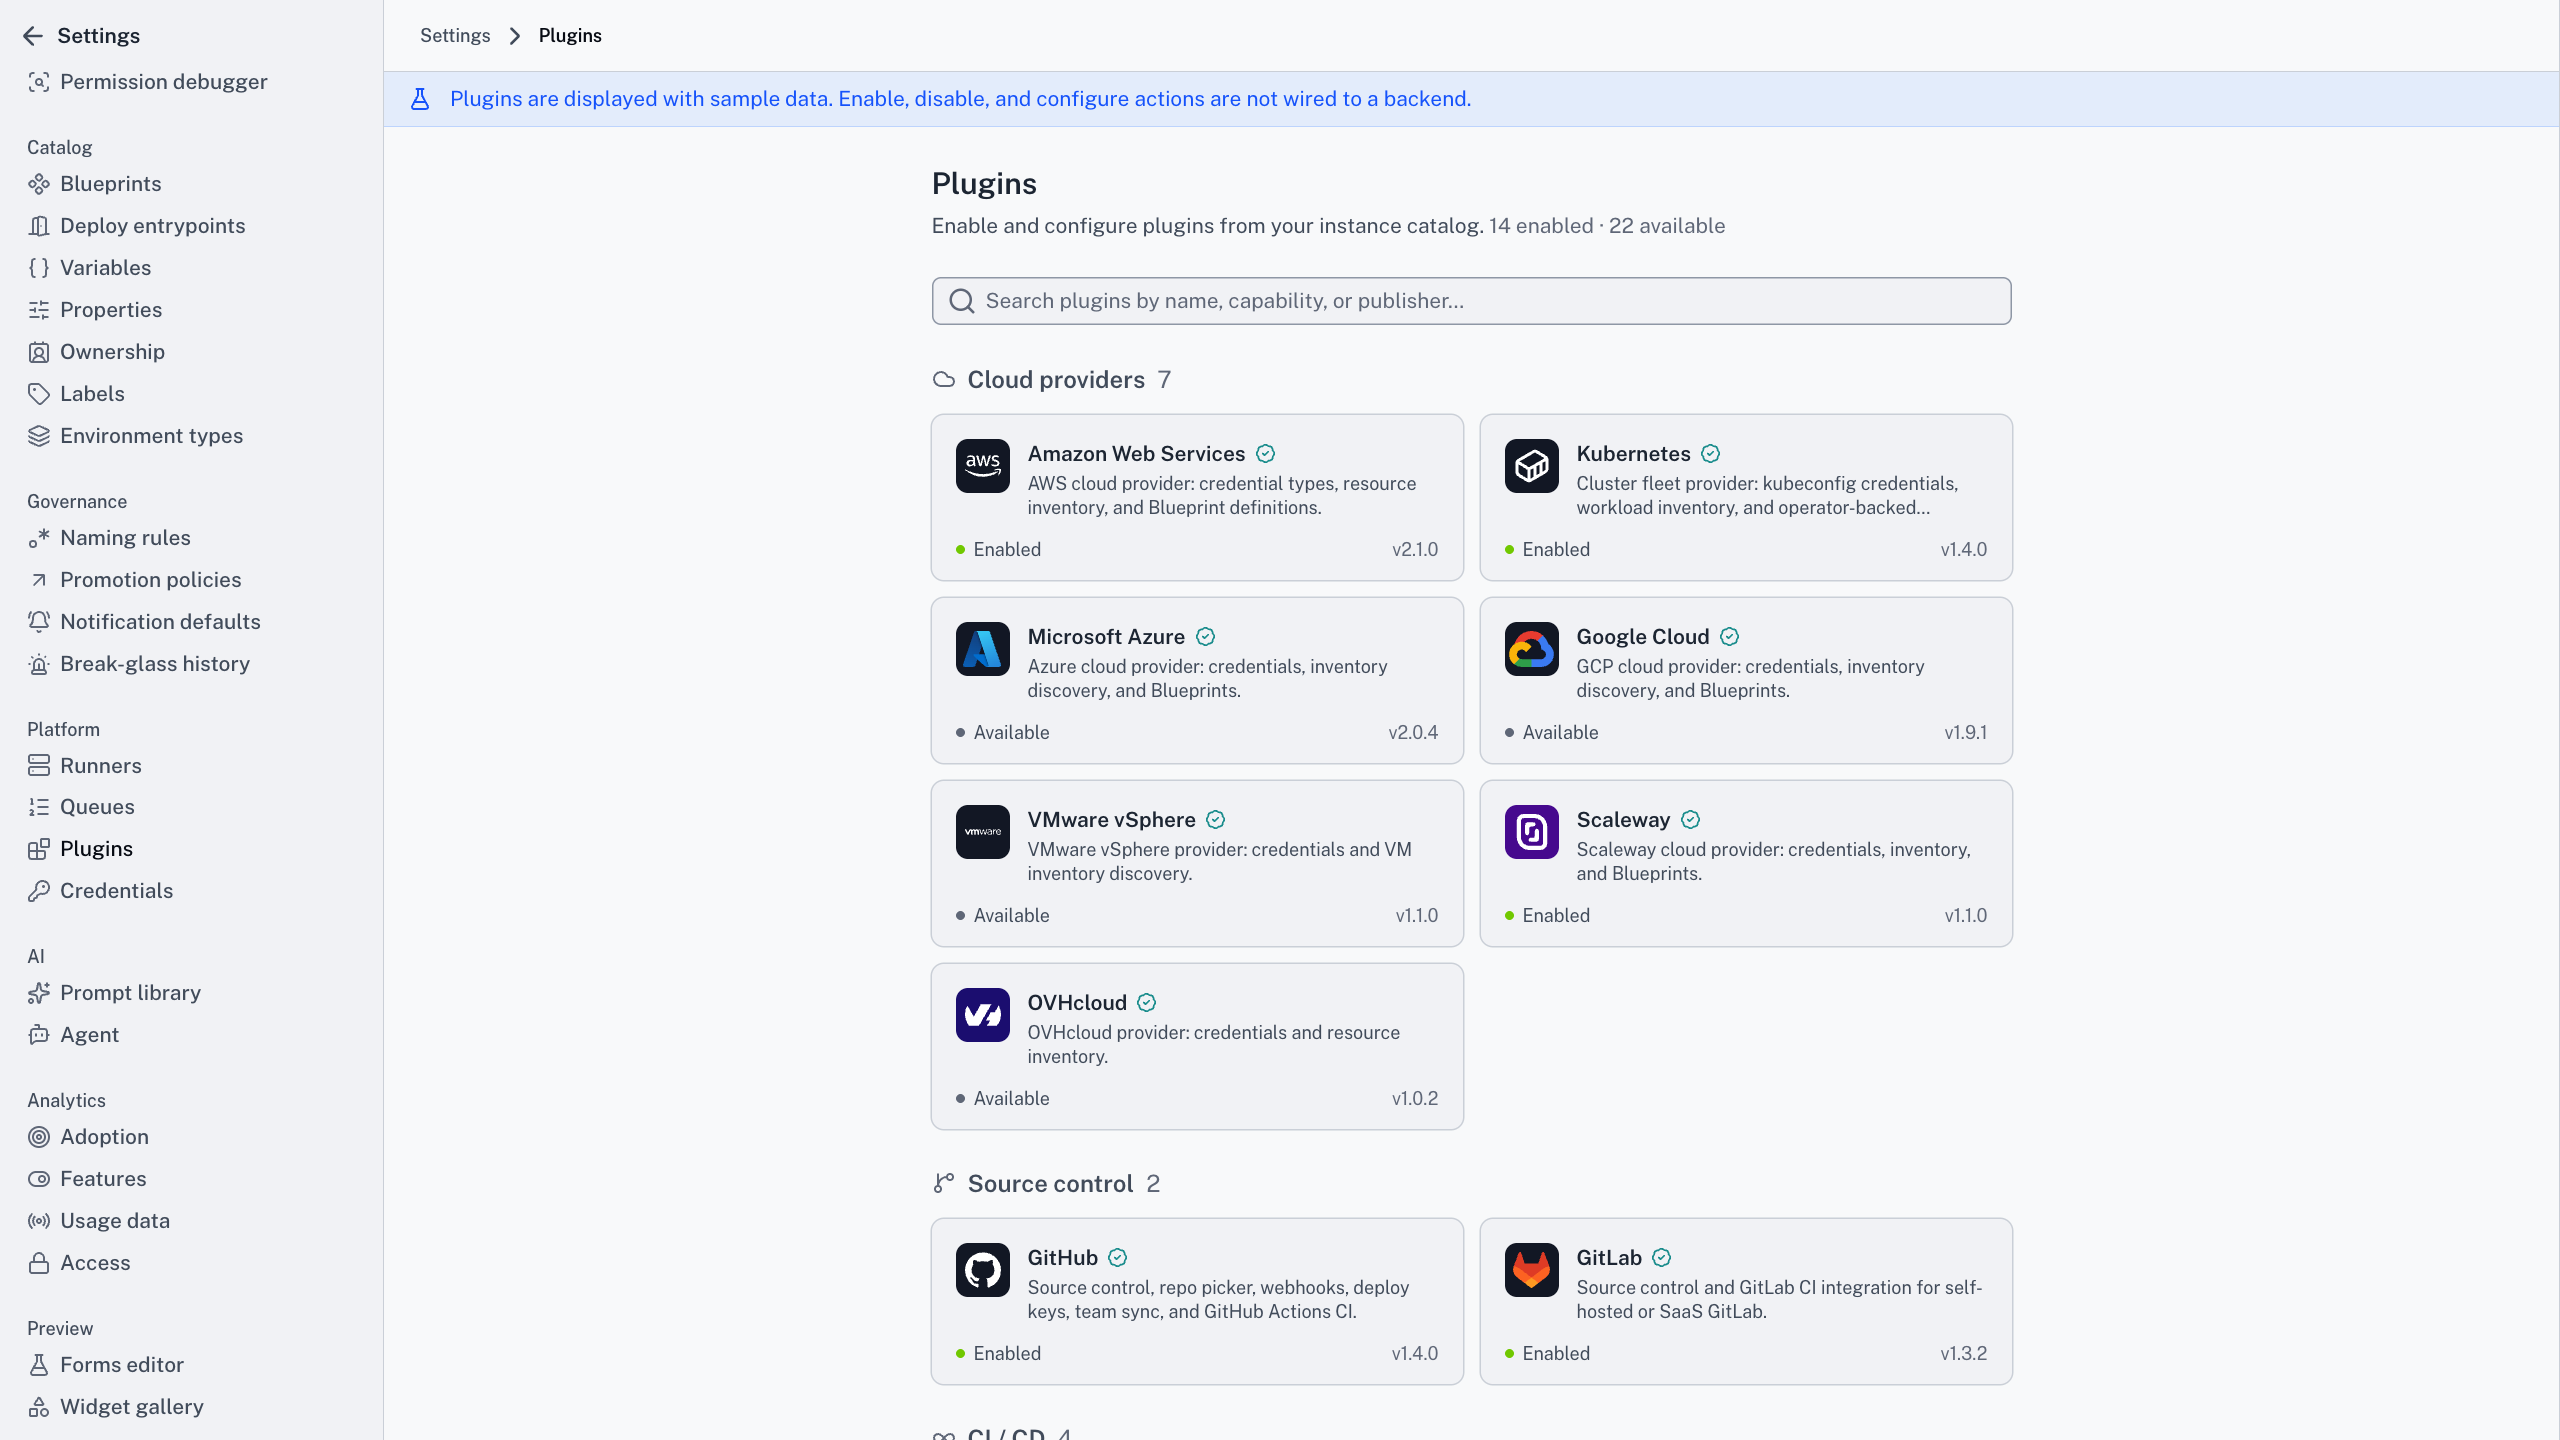
Plugins
Adds providers, data sources and widgets, official or your own, switched on per tenant.
Written in TypeScript and run in isolation. Install from the marketplace, a private registry or a tarball for air-gapped sites.
Built for
Platform & DevOps
Developers
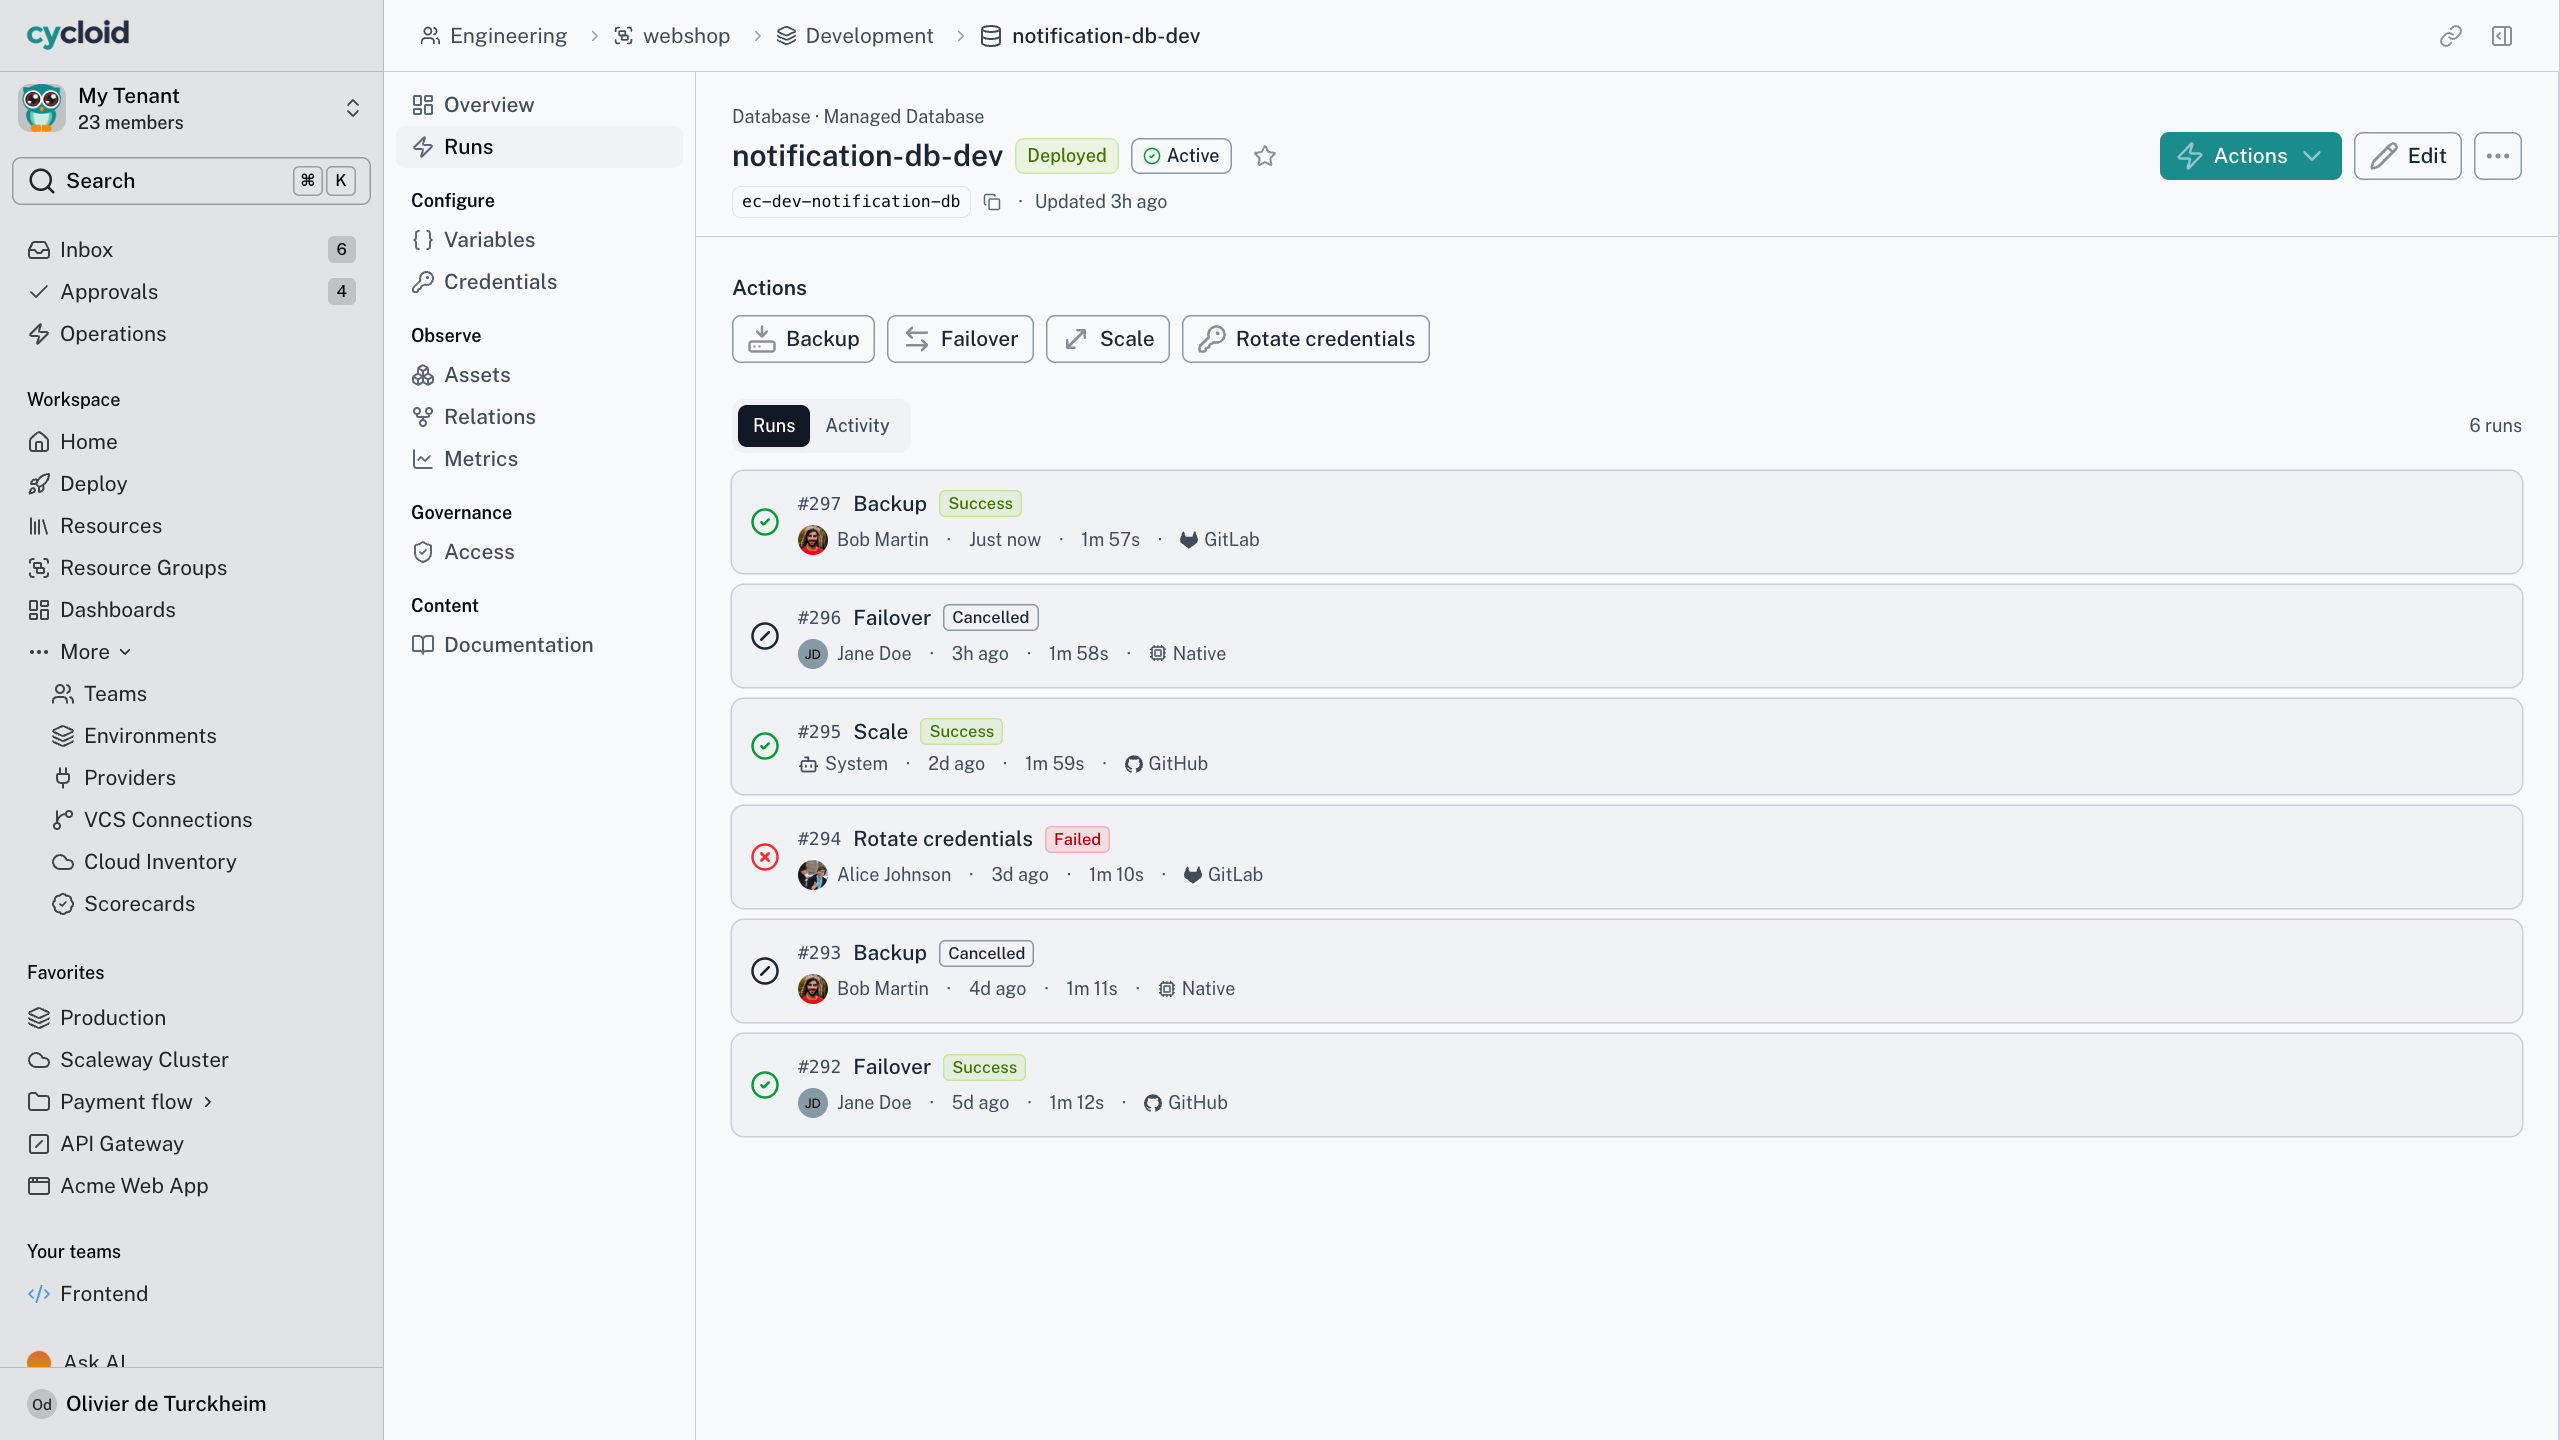
Native runner, or your CI
Executes Actions where you decide: the Native Runner inside your environment, or your existing CI.
The Native Runner runs across clouds and on-prem, or hand execution to GitHub Actions, GitLab CI, Jenkins or Azure DevOps.
Built for
Platform & DevOps
Developers
Environment types & naming rules
Built for
Executives
Platform & DevOps
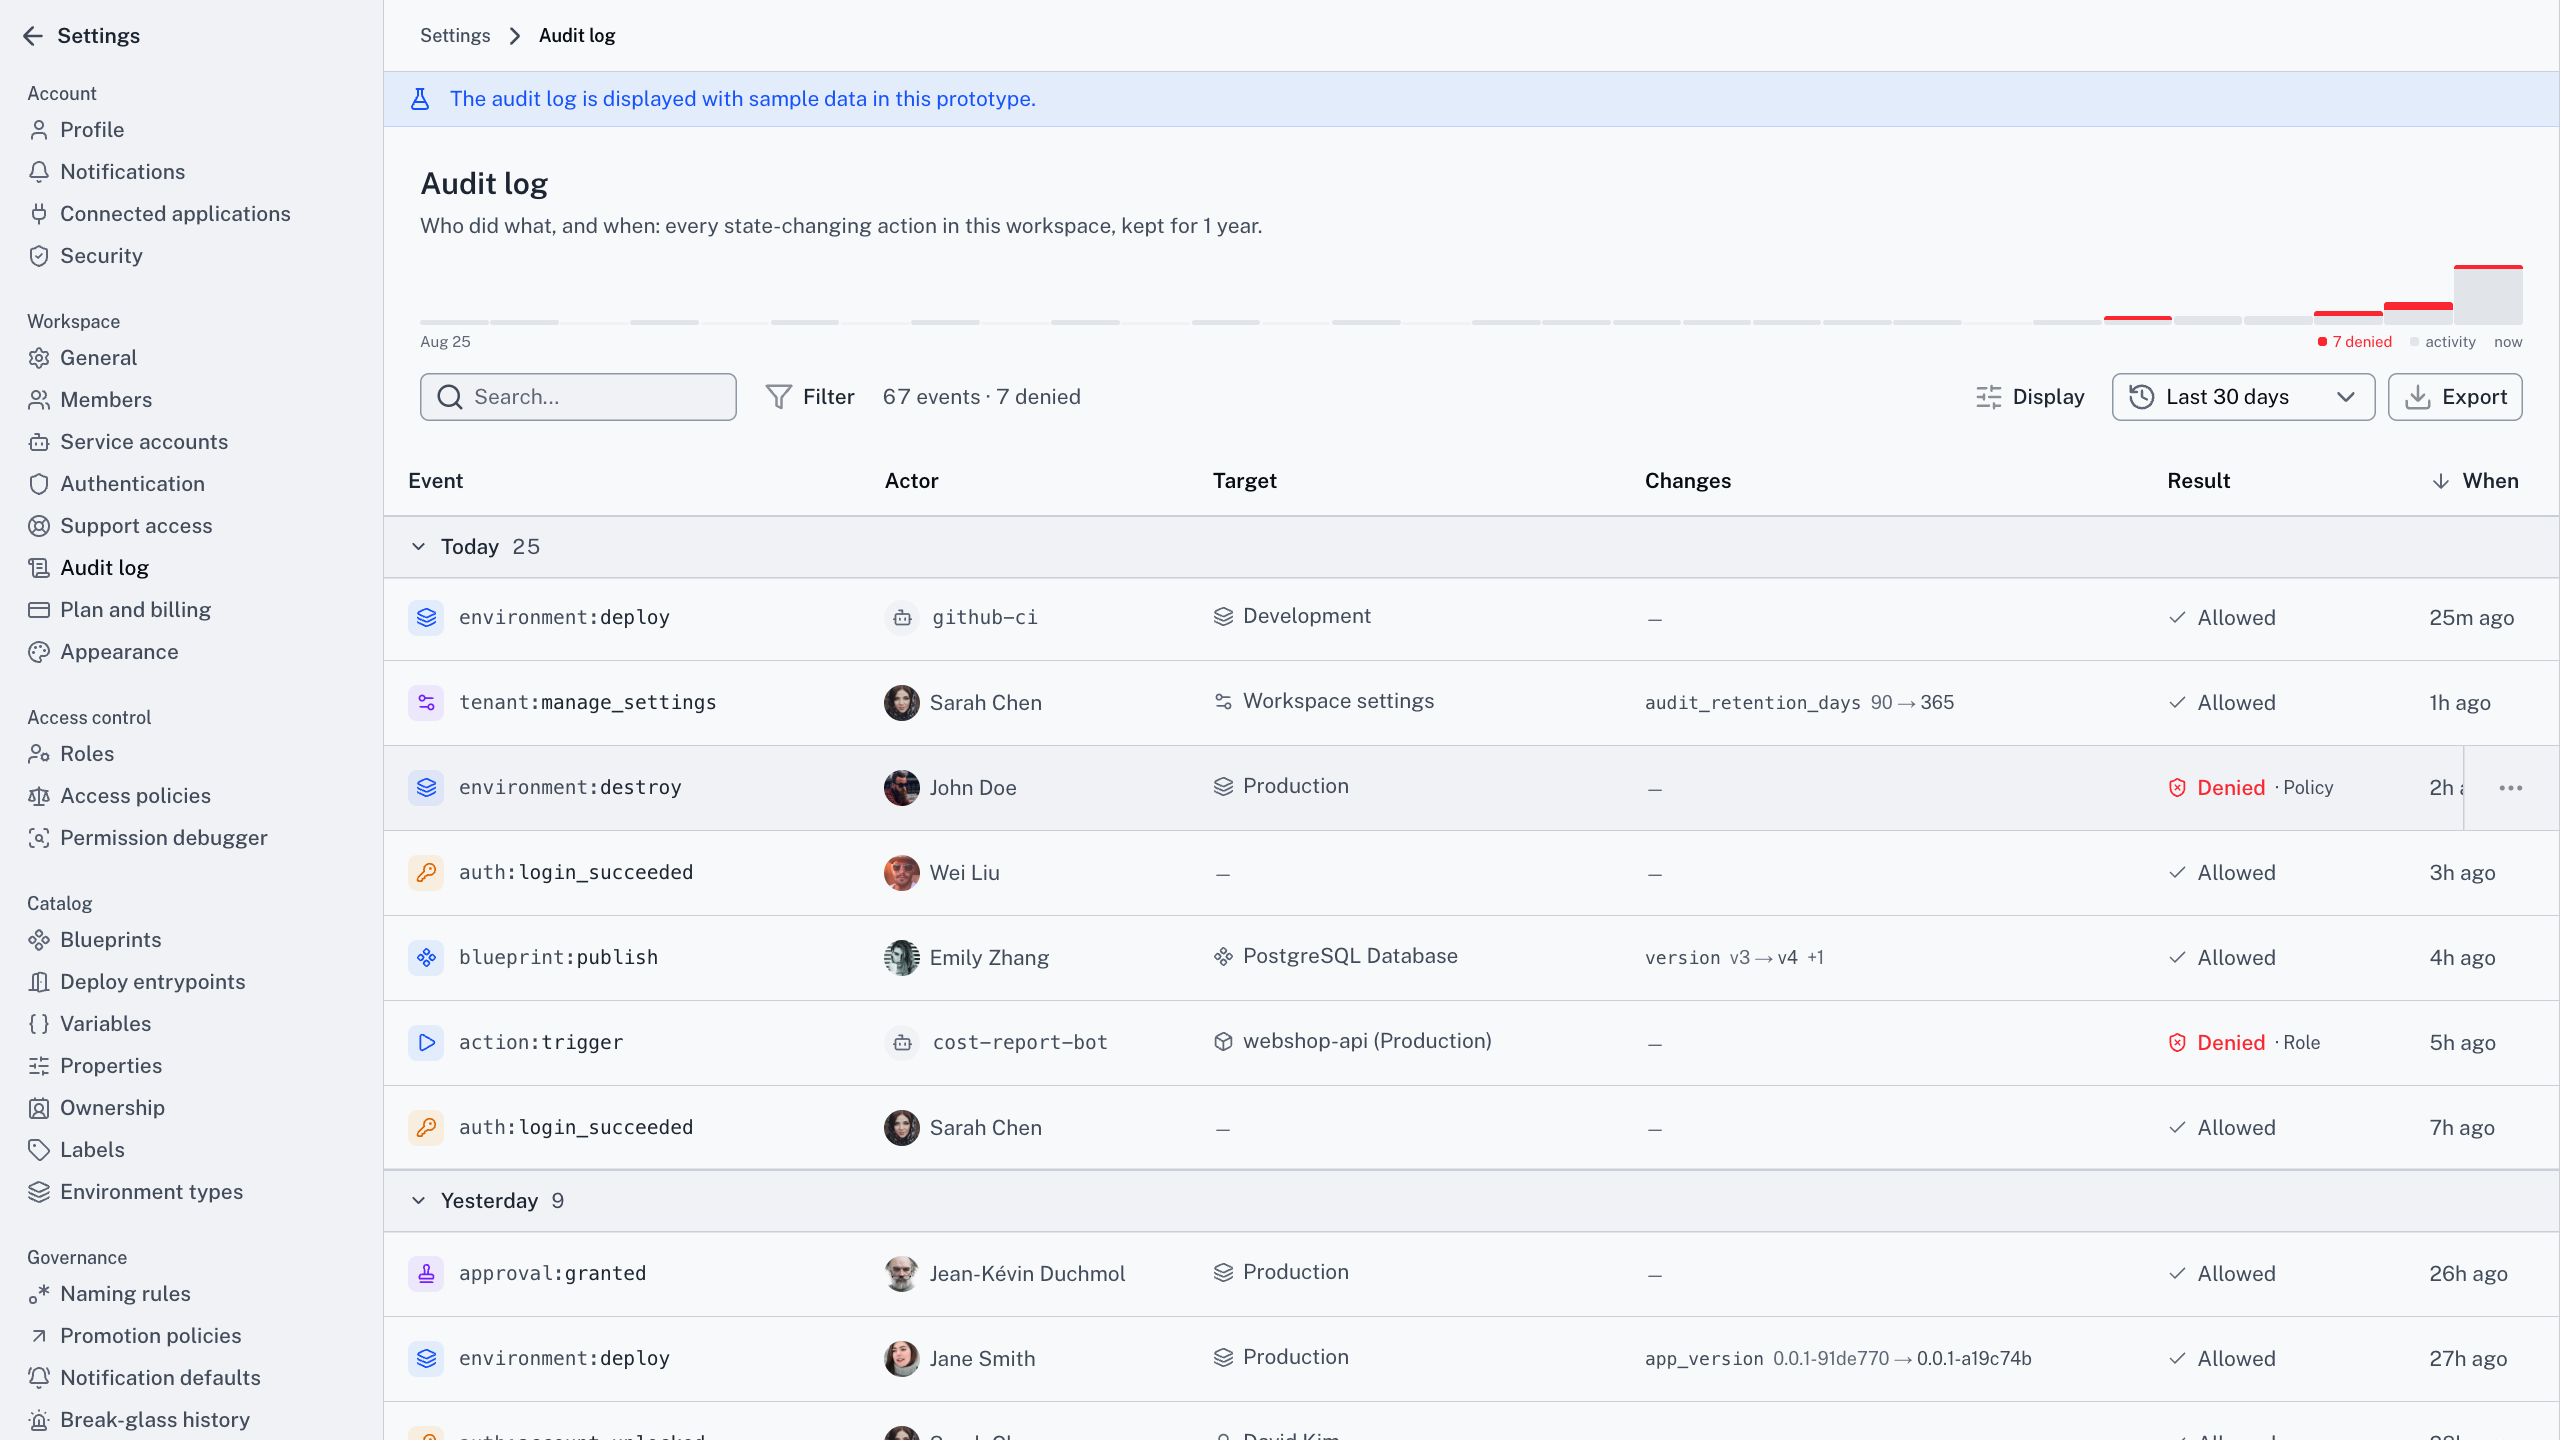
Audit log
Records every request, approval, Action and its outcome, with who or which assistant triggered it and under which authorisation.
Written by the platform as the Action runs, not a log sent from elsewhere. One request ID traces a change end to end.
Built for
Executives
Platform & DevOps
The whole picture of the Governance & Platform pillar
One path, and where it leads
Four steps, each with a page of its own. Identity first, then who may do what, then where it runs, then the record of it.
Pillar 01
Self-service that doesn’t stop at deploy: run, promote and see it all in one portal.
Bring the change that needs three sign-offs
In twenty minutes we’ll show you the guardrail that replaces them, on a self-hosted instance if that’s how you’d run it.